
Public PoC Reveals Local Root Exploit for DirtyDecrypt Linux Kernel
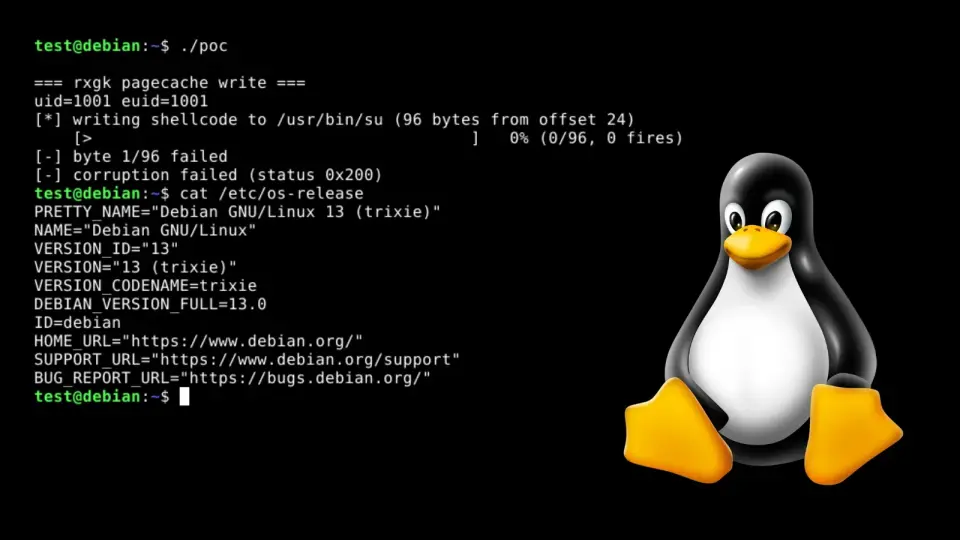
A public proof‑of‑concept exploit for the DirtyDecrypt (DirtyCBC) Linux kernel local privilege escalation (CVE-2026-31635) has been released. It exploits a missing copy-on-write guard in rxgk_decrypt_skb() within the RxGK subsystem, enabling a local unprivileged user to overwrite privileged memory (including /etc/shadow, sudoers, and SUID binaries) and gain root. The upstream patch was merged on April 25, 2026, and affected kernels require RXGK to be enabled (CONFIG_RXGK=y/m). Rolling‑release distributions with unpatched kernels (e.g., Fedora Rawhide, Arch before patch, openSUSE Tumbleweed) are at risk, while distros that ship RXGK disabled (e.g., some Debian/RHEL/Ubuntu builds) are less affected. In containers and Kubernetes environments, the flaw can lead to container escapes and host compromise. Mitigations include upgrading the kernel package and rebooting; as a temporary workaround, blacklisting rxrpc, esp4, and esp6 can be used at the expense of IPsec/AFS functionality. Kubernetes operators should rebuild worker images with patched kernels and enforce strict pod security settings.
- DirtyDecrypt Linux Kernel Vulnerability PoC Exploit Code Released CyberSecurityNews
- DirtyDecrypt PoC Released for Linux Kernel CVE-2026-31635 LPE Vulnerability The Hacker News
- Linux kernel flaw opens root-only files to unprivileged users The Register
- Exploit released for new PinTheft Arch Linux root escalation flaw BleepingComputer
- CVE-2026-46333: Local Root Privilege Escalation and Credential Disclosure in the Linux Kernel ptrace Path Qualys
Want the full story? Read the original reporting
Read on CyberSecurityNews