
FBI probes dark-web sale of 153 million IDs, including Hegseth's, linked to IDScan.net
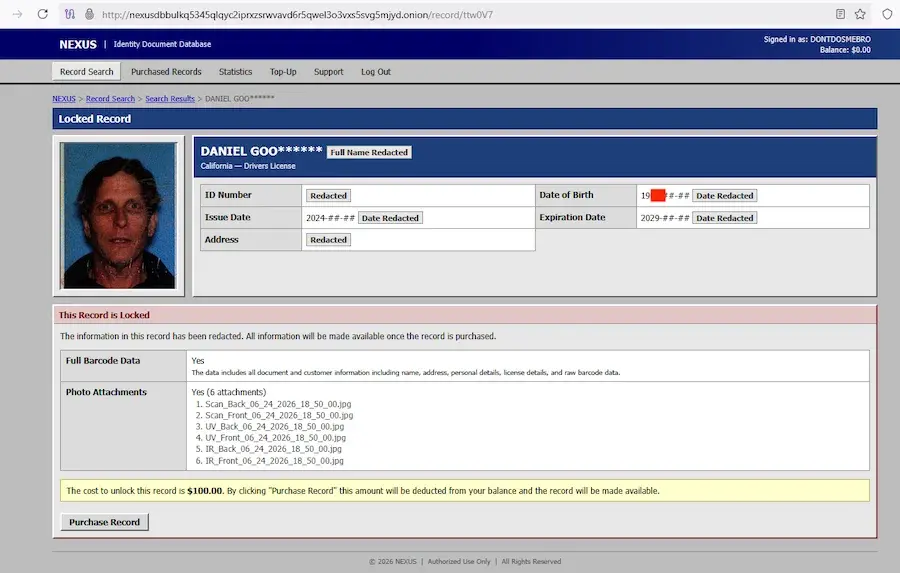
A dark-web service called Nexus is selling high-resolution scans of over 153 million US and Canadian driver's licenses, including that of US Secretary of War Pete Hegseth. The data, which includes infrared and ultraviolet images to bypass security checks, is believed to have been exfiltrated from IDScan.net, a third-party identity verification vendor. The FBI is investigating the breach, which appears to be ongoing and has affected numerous Fortune 500 clients.
Key points
- Nexus, a dark-web ID theft service, is offering scans of over 153 million driver's licenses and other IDs for as little as $100 each.
- The leaked data includes high-resolution scans in visible, infrared, and ultraviolet spectrums, potentially allowing counterfeit IDs to pass hologram tests.
- The breach is suspected to originate from IDScan.net, a New Orleans-based ID scanning service that has an exclusive arrangement with cannabis chain Planet13 and serves clients like Hertz, Shell, and FedEx.
- The FBI is investigating the incident, with the New Orleans field office looking into the data's source.
- Nexus claims to have been 'continuously exfiltrating new data for over a year,' with the number of available licenses growing by nearly 400,000 in a single day.
- The Nexus service went dark shortly after the breach was reported by KrebsOnSecurity, making it impossible for individuals to verify if their data was compromised.
Background
This incident follows a broader trend of privacy concerns regarding third-party data collection, such as the recent revocation of Flock ALR permits in Florida. It also follows a series of other high-profile data breaches, including a Dropbox hack and a leak of unreleased GTA VI footage, highlighting ongoing vulnerabilities in digital security.
How outlets are covering it
KrebsOnSecurity and Ars Technica emphasize the real-time nature of the breach and the specific vulnerability of the IDScan.net scanning process, noting that licenses were available for sale within hours of being scanned. Tom's Hardware and Protos highlight the high-profile victims, specifically naming US Secretary of War Pete Hegseth, and the extensive list of Fortune 500 companies that use IDScan.net's services, such as Shell, AMC Theaters, and DraftKings. All sources agree on the FBI's involvement and the scale of the breach, but differ in their emphasis on the specific victims and the corporate clients affected.
Why it matters
This breach exposes a critical vulnerability in the third-party identity verification ecosystem, putting the personal data of millions of Americans and Canadians at risk. The inclusion of infrared and ultraviolet scans makes it easier for criminals to create functional counterfeit IDs, potentially leading to widespread identity theft and fraud. The involvement of major corporations and government officials underscores the systemic risks posed by centralized data collection and the need for stricter data security regulations.
What to watch
The FBI is expected to continue its investigation into the source of the breach and the individuals responsible for the exfiltration. IDScan.net is also conducting its own investigation, though it has not yet provided a public statement. The disappearance of the Nexus service complicates efforts to determine the full scope of the breach, and individuals may not be able to verify if their data was compromised. The incident is likely to prompt increased scrutiny of third-party ID verification vendors and their data security practices.
- My driver's license is one of 153 million for sale on a new dark website Ars Technica
- FBI investigating 153 million US and Canadian driver’s licenses leaked on Russian cybercrime forum, including that of US SecDef Pete Hegseth — data is suspected to have come from an ID-authentication service provider Tom's Hardware
- Over 153 Million Scanned Driver's License Found For Sale On Dark Web, Some For Just $100 yahoo.com
- FBI investigates as hackers sell digital scans of 153M drivers licenses Adafruit
- 150 million IDs allegedly stolen — including Pete Hegseth’s Protos | Informed crypto news
Want the full story? Read the original reporting
Read on Ars Technica