
New DDoS Flaws Enable Attackers to Turn Domain Controllers into Botnets
TL;DR
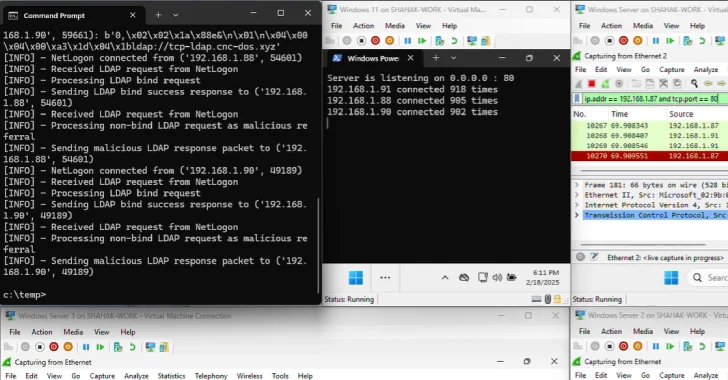
Researchers have discovered a new technique called Win-DDoS that exploits flaws in Windows LDAP and RPC protocols to turn public domain controllers into a powerful botnet for DDoS attacks, without requiring code execution or credentials, and identified multiple related DoS vulnerabilities that can be exploited remotely or internally, challenging assumptions about internal system safety.
Topics:technologynetwork-security#ddos#domain-controllers#ldap#network-security#vulnerabilities#win-ddos
Want the full story? Read the original reporting
Read on The Hacker News