
"Outlook Vulnerability Exposes NTLM Passwords, Researchers Find"
TL;DR
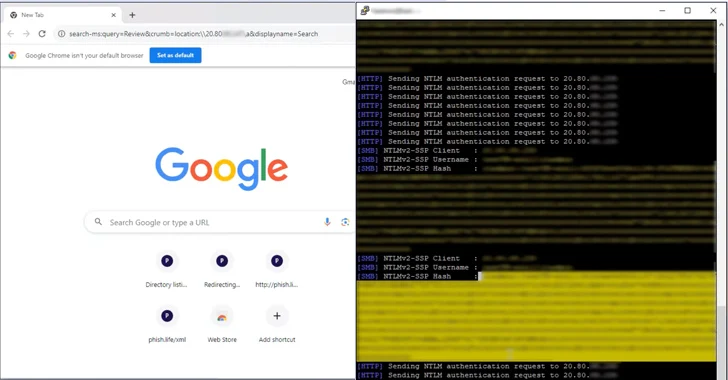
A security flaw in Microsoft Outlook, tracked as CVE-2023-35636, could allow threat actors to access NT LAN Manager (NTLM) v2 hashed passwords when opening a specially crafted file, potentially through email or web-based attack scenarios. The vulnerability, now patched, was discovered by Varonis security researcher Dolev Taler and could lead to NTLM hashes being leaked. Microsoft has announced plans to discontinue NTLM in Windows 11 in favor of Kerberos for improved security.
Topics:technologytechnologysecurity#microsoft-outlook#ntlm#patch-tuesday#security-flaw#technologysecurity#vulnerability
Want the full story? Read the original reporting
Read on The Hacker News