
Nearby attackers can crash AirDrop and Quick Share, researchers warn
TL;DR
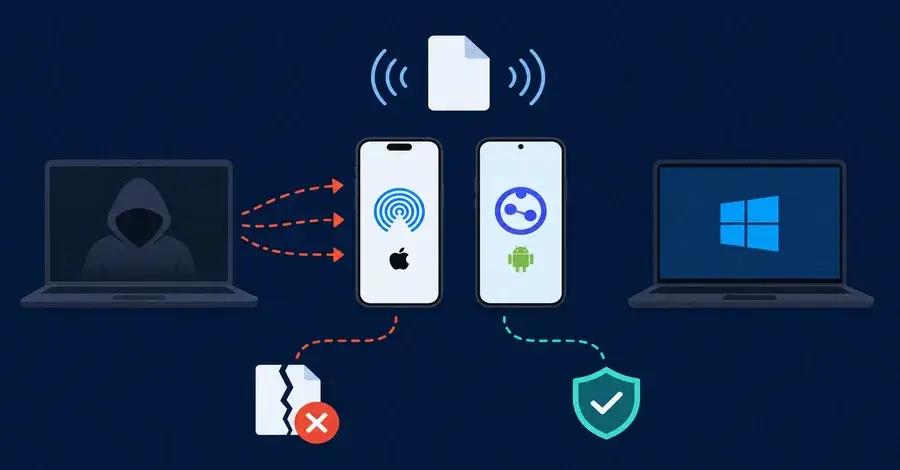
Researchers disclosed six local flaws in AirDrop and Quick Share that let nearby attackers crash the receiving devices or bypass session checks. Apple and Google have begun patching these flaws (Apple has assigned a CVE; Google fixed the Windows Quick Share bug; Samsung’s issues are under investigation). The exploits are local (about 10–30 meters or on the same LAN) and affect macOS/iOS, Samsung Quick Share, and Windows Quick Share. Users should update to the latest OS and adjust AirDrop to Contacts Only or disable Everyone, and limit Quick Share visibility when not actively receiving.
Topics:top-newstechnology#airdrop#cross-platform#cve#quick-share#security-vulnerabilities#technology
Want the full story? Read the original reporting
Read on The Hacker News