
AdFection: How Ad Networks Enabled Zero-Click Spyware Attacks
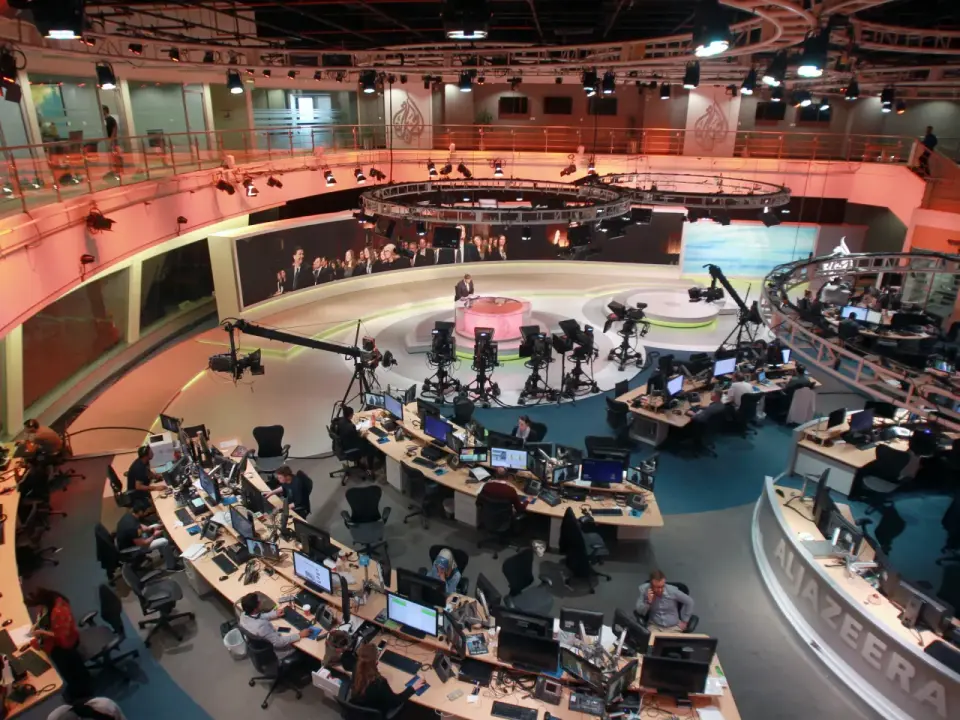
Citizen Lab has confirmed the first known instance of 'AdFection,' a zero-click spyware attack delivered via targeted online advertisements. The campaign, facilitated by Israeli firm Discover-Tech and spyware vendor Candiru, infected 45 devices belonging to Al Jazeera staff in 2024 and 2025. By exploiting real-time bidding infrastructure, attackers could automatically install malware without user interaction, targeting high-profile individuals across government and media networks. Major ad platforms, including Google and Beeswax, have since banned Discover-Tech, though experts warn the structural design of the ad ecosystem remains vulnerable to similar abuses.
Key points
- Citizen Lab confirmed the first public technical evidence of 'AdFection,' a zero-click spyware campaign delivered through targeted online ads.
- The attack was facilitated by Israeli firm Discover-Tech and spyware vendor Candiru, infecting 45 devices belonging to Al Jazeera staff in 2024 and 2025.
- Discover-Tech used a platform called Controlium to mass-profile and deanonymize users, then covertly hack targets with third-party spyware.
- Major ad platforms, including Google, IAB Europe, Beeswax, Vungle, and Eskimi, have since banned or paused Discover-Tech's access to their networks.
- Experts warn that the structural design of the online advertising ecosystem remains vulnerable to similar surveillance abuses, calling for regulatory intervention.
Background
This incident follows earlier zero-click attacks, such as the AI-assisted WeChat worm 'WeWorm' disclosed in September 2026, which highlighted vulnerabilities in digital infrastructure. The AdFection campaign underscores growing concerns about the weaponization of online advertising for surveillance, building on previous reports of ad tech being used for tracking and profiling.
How outlets are covering it
Citizen Lab and The Guardian emphasize the structural flaws in the online advertising ecosystem, noting that major ad vendors failed to detect or prevent Discover-Tech's malicious operations for years. Ars Technica highlights the technical sophistication of the zero-click exploits, stressing that the attacks were invisible unless users ran special forensic tools. Al Jazeera condemned the targeting of its staff, calling for accountability, while cybersecurity analysts like Eddy Willems and Stephen O'Shaughnessy warned that the ad system's design makes it inherently vulnerable to such abuses. Confiant's separate report corroborated the targeting of government and international organization networks, though it noted that infection was not confirmed in all cases, only profiling.
Why it matters
The AdFection campaign represents a significant escalation in cyber threats, demonstrating how everyday online activities, such as browsing websites or using apps, can be exploited to install sophisticated spyware without user interaction. This poses a global security risk, particularly for journalists, government officials, and activists, and highlights the need for stricter regulation and vetting within the online advertising industry to prevent similar abuses in the future.
What to watch
Regulators and lawmakers in the US, Europe, and other regions are expected to investigate Discover-Tech and Candiru for potential violations of applicable laws. The advertising industry is urged to implement stricter vetting processes for ad vendors, while users are advised to install ad blockers, reset mobile advertising IDs, and keep devices updated to mitigate risks. Citizen Lab is also working with vendors to mitigate the mass-deanonymization attack by a threat actor called DARK CARTOGRAPHER, which is using Discover-Tech's infrastructure to link device advertising IDs with phone numbers.
- How Israeli firm’s ‘zero-click’ malware attack poses global security risk Al Jazeera
- Exposing AdFection: How Discover-Tech Turned Targeted Ads Into a Pipeline for Zero-Click Mercenary Spyware The Citizen Lab
- Online ads weaponised to deliver ‘zero-click’ spyware, researchers say The Guardian
- Targeted ads delivered 0-click exploits to install mercenary malware Ars Technica
- Israeli firm used online ads to run vast spy operation, researchers say Reuters
Want the full story? Read the original reporting
Read on Al Jazeera