cybersecurity16 min read
Security Firm Exposes 'Adception' Scam Using Google and Bing to Distribute Malicious Claude Installer
15 hours ago•Source: Fox News
View original source
The latest cybersecurity stories, each synthesized from multiple sources with added background and context.
Threat actors exploited a compromised credential for ConnectWise Cloud Backup to access 173 Microsoft 365 tenants. The breach allows attackers to read mail, files, and directory data, with some tenants showing unauthorized privilege escalation. ConnectWise has suspended the application pending investigation.
BleepingComputer•1 day ago
Al Jazeera•1 day ago
Researchers at The Citizen Lab have disclosed the first public technical evidence of 'AdFection,' a zero-click spyware campaign delivered through targeted online ads. The attack, attributed to the Israeli firm Discover-Tech and spyware vendor Candiru, infected 45 devices belonging to Al Jazeera in 2024 and 2025. By exploiting real-time bidding infrastructure, attackers could automatically install malware without user interaction. Major ad platforms, including Google and Beeswax, have since banned Discover-Tech, though experts warn that the structural design of the ad ecosystem remains vulnerable to similar abuses.
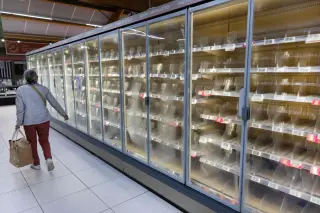
A second wave of cyberattacks hit French supermarkets on Monday night, targeting Dixell refrigeration systems after a previous day's breach of Danfoss equipment. The attacks, which altered temperature settings to extreme levels, affected hundreds of stores across major chains but caused no food waste in the latest incident due to rapid response. French authorities are investigating the coordinated attacks, which have raised concerns about the security of connected food supply systems.
Microsoft’s October 2026 security update resolves 1,413 vulnerabilities, surpassing the September record. The release includes 80 critical flaws and two zero-days, with one actively exploited in the wild. Security experts advise prioritizing exploitable risks over total volume, noting that AI-driven discovery is accelerating bug fixes but not necessarily exploitation rates.
Ledger has confirmed that unauthorized hardware implants were found in its Nano X devices sold through the Southeast Asian reseller CryptoBilis, leading to the theft of approximately $102 million in cryptocurrency. The implants, which capture seed phrases and transmit them via LTE, have been identified in multiple variants, with some appearing in devices sold through authorized European retailers like MediaMarkt. Ledger has paused sales through CryptoBilis and other affected resellers, advising users to move assets to new devices. While Ledger states its core infrastructure remains secure, the incident has raised concerns about the integrity of its authorized reseller network and the sophistication of the attackers.
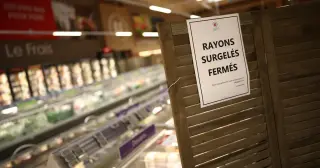
A large-scale cyberattack disrupted refrigeration systems in hundreds of French supermarkets, forcing fridges and freezers to heat to 50C overnight. The incident caused fires, massive food spoilage, and estimated losses of millions of euros. Paris prosecutors have opened an investigation into the attack, which targeted legacy software from Danish manufacturer Danfoss.
A large-scale cyberattack disrupted refrigeration systems in hundreds of French supermarkets, forcing fridges to heat to 50C and causing fires and significant food waste. The attack targeted legacy software from Danish manufacturer Danfoss, affecting chains like Intermarché and Coopérative U. While the full scope remains unclear, similar issues were reported in the Netherlands, prompting EU-wide security concerns.
GitLab released emergency patches on October 8 for a maximum-severity vulnerability (CVE-2026-97229) in its CI/CD regular expression compiler. The flaw, rated 10.0 on the CVSS scale, allows unauthenticated attackers to execute arbitrary code via specially crafted regex inputs. Self-managed users must upgrade to versions 19.2.8, 19.3.4, or 19.4.2 immediately; cloud-hosted instances are already patched.
Calendar invitation scams have surged exponentially, with attacks increasing tenfold in August alone. These schemes exploit the trust users place in calendar entries, using AI to create convincing fake meetings or deepfake video calls. Unlike standard email, calendar invites can auto-accept, bypassing spam filters. Experts warn that AI agents may soon auto-accept these fraudulent invites, while passkeys are cited as the primary defense against credential theft.
A coordinated cyberattack has disrupted refrigeration systems across major French supermarket chains, causing temperatures to spike to 50C and resulting in the disposal of millions of euros worth of food. The Paris prosecutor's office has opened an investigation into the incident, which affected stores from Intermarché, Coopérative U, and potentially other major retailers.
Canadian cybersecurity executive Edward Dubrovsky was arrested in Pennsylvania and faces federal charges for conspiracy and extortion. The FBI links the arrest to the ShinyHunters hacking group, which recently breached agency personnel data. Dubrovsky previously worked for firms that negotiate ransomware payments for victims, raising questions about the boundaries of cyber negotiation services.