
Australian authorities arrest two suspects in TeamPCP supply-chain attack campaign
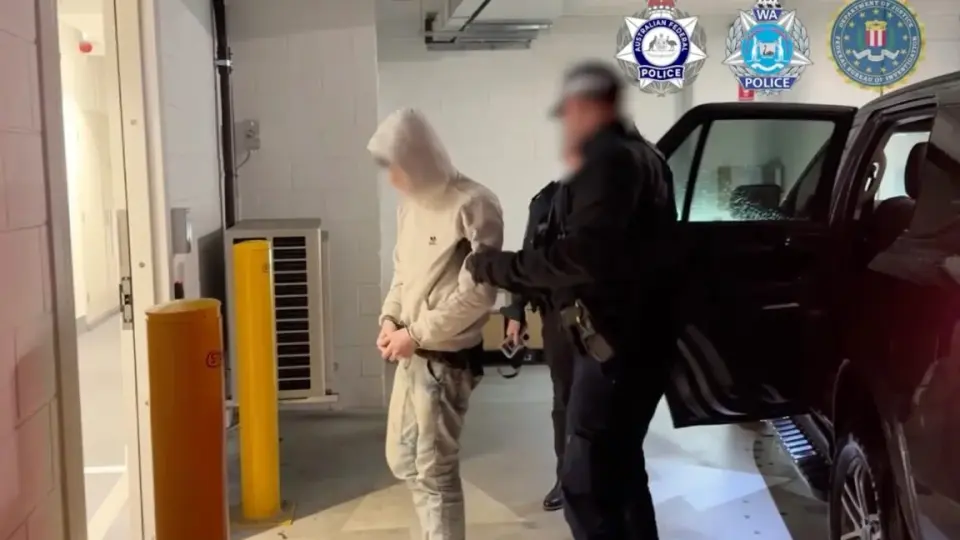
The Australian Federal Police arrested two men from Western Australia accused of participating in TeamPCP, a cybercrime group responsible for a nine-month campaign of supply-chain attacks. The group infected over 1,000 organizations using a self-propagating worm called Shai-Hulud, which targeted open-source software and CI/CD pipelines. While the AFP did not name the suspects, investigative reporting identifies one as a 21-year-old man linked to multiple cybercrime forums and a neo-Nazi network. The arrests follow a series of high-profile compromises, including attacks on AI infrastructure and popular developer tools, with the suspects facing potential prison sentences of over 10 and 20 years.
Key points
- The Australian Federal Police arrested two men from Cottesloe and Mandurah, Western Australia, and charged them with 14 offenses related to TeamPCP.
- TeamPCP is accused of compromising over 1,000 organizations worldwide through a sustained supply-chain attack campaign lasting nine months.
- The group utilized a worm dubbed Shai-Hulud, which infected open-source packages and self-propagated by stealing credentials from CI/CD pipelines.
- KrebsOnSecurity identifies one suspect as a 21-year-old man with a history of cybercrime forum activity and links to a neo-Nazi network, while the AFP did not publicly name the defendants.
- Potential prison sentences for the two men range from over 10 years to more than 20 years if convicted.
Background
TeamPCP emerged in late 2025 as a significant threat in the cybersecurity landscape, distinct from traditional structured criminal crews. According to Google Threat Intelligence, the group functions as a peer community of individually skilled actors rather than a single organized entity. The group’s operations have been linked to a broader network of cybercriminals who collaborate through platforms like the 'Cybercats' Matrix chat server. Previous coverage highlighted the group’s involvement in data extortion and the compromise of major technology infrastructure, including AI gateways and developer tools, marking it as one of the most prolific supply-chain attackers in recent history.
How outlets are covering it
Ars Technica emphasizes the scale of the operation, noting that TeamPCP infected over 1,000 organizations and highlighting the viral nature of the Shai-Hulud worm, which exploited CI/CD pipelines. KrebsOnSecurity provides a detailed investigative profile, identifying the suspects through open-source intelligence and highlighting operational security failures, such as the use of real names in company registrations and forum posts. Krebs also notes the role of AI in compressing the time required for such sophisticated attacks, a point supported by Aikido Security researcher Charlie Eriksen. While Ars Technica focuses on the technical mechanics of the worm, KrebsOnSecurity focuses on the human element and the 'rogue' nature of the group’s leadership. Yahoo’s coverage, while largely obscured by technical code in the provided text, aligns with the narrative of a 'rookie mistake' leading to the arrests, emphasizing the lack of operational discipline among the hackers.
Why it matters
The arrests of TeamPCP members signal a significant law enforcement response to the growing threat of supply-chain attacks in the open-source ecosystem. The Shai-Hulud worm’s ability to self-propagate through CI/CD pipelines represents a new and dangerous vector for malware distribution, potentially compromising the integrity of software used by thousands of organizations. The case highlights the vulnerabilities of modern software development practices and the need for enhanced security measures in package management and credential handling. Furthermore, the identification of the suspects through open-source intelligence underscores the importance of operational security for cybercriminals and the effectiveness of international cooperation in combating cybercrime.
What to watch
The two arrested men are expected to appear in court in Perth, Western Australia, where they will face 14 charges. If convicted, one suspect faces a potential sentence of more than 20 years in prison, while the other faces over 10 years. Security experts are likely to continue monitoring for any residual activity from TeamPCP or related groups, as the arrests may not dismantle the entire network. Organizations that were compromised by the Shai-Hulud worm are advised to audit their CI/CD pipelines and rotate credentials to mitigate any ongoing risks. The case may also prompt further scrutiny of open-source software supply chains and the use of AI in cybercrime operations.
- Authorities arrest 2 alleged members of prolific hacking group TeamPCP Ars Technica
- Two Alleged ‘TeamPCP’ Hackers Arrested in Australia Krebs on Security
- Rookie Mistake: Hacker's Attachment to Screen Name Made Him Easy to Catch Yahoo
- TeamPCP arrests don't fix the supply chain risk they exposed Aikido Security
- Two alleged TeamPCP members arrested and charged after months of software supply-chain chaos CyberScoop
Want the full story? Read the original reporting
Read on Ars Technica