
ClawJacked WebSocket Flaw Lets Local OpenClaw AI Agents Be Hijacked
TL;DR
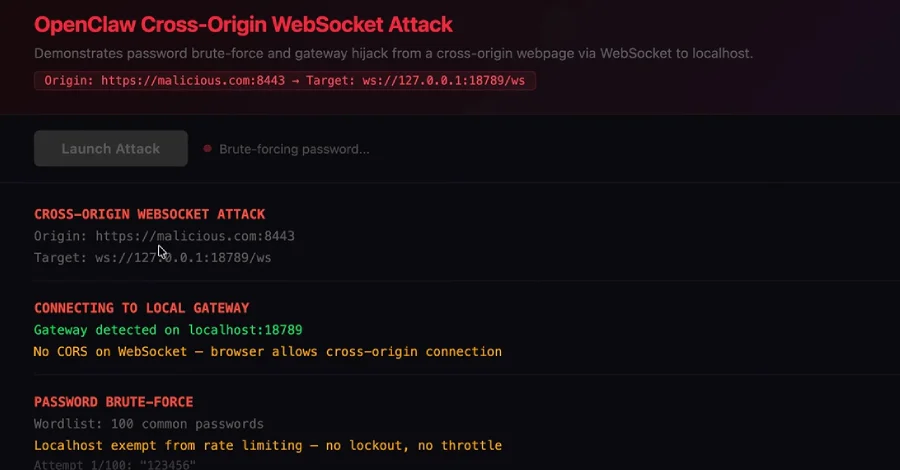
OpenClaw fixed a high-severity vulnerability, dubbed ClawJacked, that let a malicious website abuse a local WebSocket connection to a localhost OpenClaw gateway, brute-force its password, and auto-approve as a trusted device to gain full control over a locally running AI agent. A patch was released in version 2026.2.25 (Feb 26, 2026); users should update and audit access to AI agents. The story sits in a broader context of AI-agent attack surfaces, prior log-poisoning fixes (2026.2.13), related CVEs, and a surge in malicious skills on ClawHub, highlighting the need for isolation, governance, and vigilance against prompt injections.
- ClawJacked Flaw Lets Malicious Sites Hijack Local OpenClaw AI Agents via WebSocket The Hacker News
- OpenClaw: What is it and can you use it safely? Malwarebytes
- I built an OpenClaw AI agent to do my job for me. The results were surprising—and a little scary Fast Company
- The hidden risks behind Microsoft’s OpenClaw TechRadar
- 5 Things You Need to Know Before Using OpenClaw KDnuggets
Want the full story? Read the original reporting
Read on The Hacker News