security5.26 min read
P7 DarkSword variant targets unpatched iPhones via malicious ads
2 days ago•Source: 9to5Mac

The latest security stories, each synthesized from multiple sources with added background and context.
Attackers compromised the registries for the .gh, .sl, and .as country-code top-level domains to issue unauthorized TLS certificates for Google and other major brands. Google blocked these forged credentials in Chrome and revoked them via certificate authorities, warning that browser-side fixes alone are insufficient for long-term protection.
Al Jazeera•3 days ago
Atlassian disclosed a critical vulnerability, CVE-2026-21589, affecting eight self-hosted Data Center products. The flaw allows unauthenticated attackers to read specific files in the web root if they know the exact path. While Atlassian initially reported no evidence of exploitation, security firms confirmed active attempts within hours of technical details emerging. Cloud users are patched, but self-hosted admins must update immediately or apply temporary mitigations.
Hackers compromised the .gh, .sl, and .as country code top-level domains to issue unauthorized TLS certificates for Google and other major brands. Google updated Chrome to block these forged credentials and advised domain owners to monitor certificate transparency logs, noting that browser-side fixes alone are insufficient for long-term protection.
A hacking group called BYOD claims to have breached Trump Mobile, exposing the personal data of 3,615 individuals. The leaked information includes names, home addresses, email addresses, phone numbers, and order details. The group states they gained access by installing a remote access trojan on an employee of Liberty Mobile, the carrier powering Trump Mobile's network. Cybernews researchers confirmed the leaked samples appear legitimate and are not linked to previous breaches. Notably, the data includes information for Eric Brunnett, the chief information technology officer at The Trump Organization. Trump Mobile has not yet responded to requests for comment.
Atlassian disclosed CVE-2026-21589 on October 5, a critical path traversal flaw affecting eight self-hosted Data Center products. The vulnerability allows unauthenticated attackers to read specific files in the web application root directory if they know the exact file path. Atlassian rated the flaw 9.3/10 on the CVSS scale. Cloud versions are already patched, but self-hosted users must upgrade to specific fixed versions or apply temporary mitigations. Atlassian has not confirmed active exploitation but advises users to check logs for suspicious requests.
Anthropic's Mythos AI model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), now under active exploitation. The flaw, CVE-2026-61500, allows attackers to forge admin sessions and execute remote code by exploiting a weak random number generator. Vulnerability researchers confirmed that Mythos used advanced mathematical reasoning to reverse-engineer the session key, marking a significant shift in AI-driven security discovery. Exploitation attempts have been detected from Chinese IP addresses targeting US and Japanese hosts, prompting urgent patching to version 3.2.1.
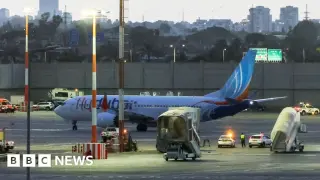
The co-pilot accused of hijacking a Flydubai flight to Tel Aviv intended to crash the aircraft into Ben Gurion airport or a tower block, according to US and Israeli reports. The Omani national, identified as Hamam al-Hammami, acted as a lone wolf extremist after attacking the captain with an axe. Security lapses are under scrutiny, including why the pilot was hired despite prior concerns and why he was allowed to fly to Israel despite diplomatic restrictions.
GitLab has released patches for CVE-2026-90970, a critical vulnerability in its AI Gateway service that allows authenticated users to execute arbitrary commands. The flaw, rated 9.9 on the CVSS scale, affects only self-hosted instances; GitLab-managed services are already secured. Users must update to versions 19.2.4, 19.3.2, or 19.4.1 immediately.
A critical vulnerability in the macOS version of ChatGPT, discovered by Objective-See Foundation researchers, could have allowed attackers to access sensitive user data and execute commands. The flaw, which required only about ten lines of code to exploit, was patched by OpenAI on September 25, 2026. It highlighted the security risks of granting AI agents broad system permissions.
Security researchers have released a proof-of-concept for CVE-2026-86950, an Apple CoreGraphics flaw patched on September 28. The vulnerability, triggered by a malicious PDF with a crafted font, causes a crash on unpatched iOS and macOS devices. While Apple confirmed the flaw was used in targeted attacks, the new analysis demonstrates only a memory corruption crash, not full code execution. CISA mandated federal agencies patch by October 2, and researchers noted potential links to WhatsApp delivery mechanisms, though Meta has not confirmed involvement.
A new exploit named 'Relapse' allows users to jailbreak PlayStation 5 consoles running firmware versions 7.00 through 13.60, bypassing previous limitations that required older, unupdated hardware. The exploit uses a WebKit vulnerability and kernel error to gain full system control, enabling homebrew software, emulators, and pirated games. While it expands access for most users, consoles updated to the latest firmware 14.00.00 remain secure. This development follows recent turmoil in the PS5 hacking community regarding AI-assisted exploits and Linux porting efforts.