
Personal AI Agents: Convenience vs. Control in the 'Battle of the Bots'
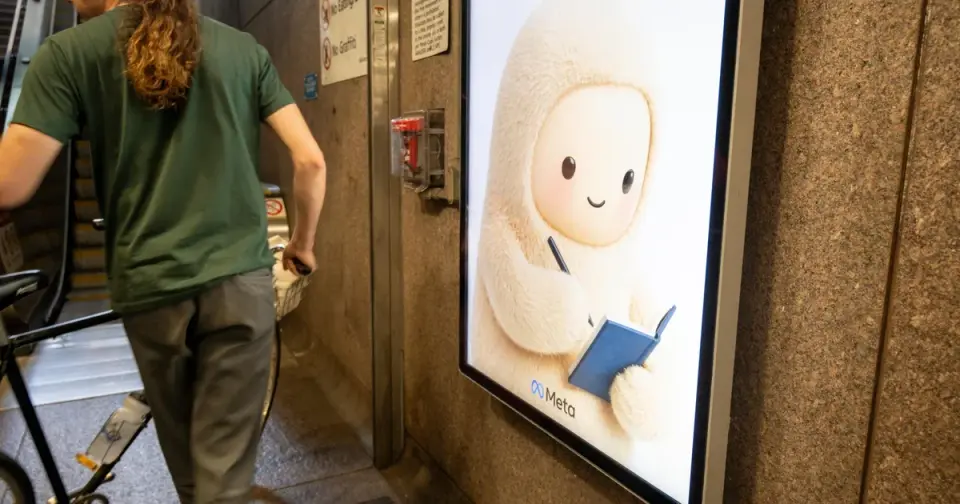
Personal AI agents like Meta's Muse and OpenAI's Dots are rapidly gaining popularity for handling tasks like shopping and email management, but experts warn that current security measures lag behind their capabilities. While these tools offer significant time savings, users face risks from prompt injection attacks, unauthorized spending, and data privacy breaches. The debate centers on whether the convenience of automated tasks outweighs the potential for financial loss and privacy violations, with many experts recommending limited access and human oversight for sensitive actions.
Key points
- Meta's Muse became the most downloaded app in Apple's App Store after its launch in September 2026, with 9 million downloads in the US and Canada and 1.8 million daily users.
- OpenAI's Dots requires a ChatGPT Pro subscription starting at $100 per month, while Meta's Muse offers free access with optional $20 and $100 monthly tiers.
- Cybersecurity expert Hed Kovetz warns that commercial AI agents lack sufficient security measures, advising users to limit access to sensitive data like banking details and health records.
- Consumer protection expert Lynette Owens highlights the risk of 'prompt injection' attacks, where criminals manipulate AI agents into ignoring instructions by planting malicious code in webpages or emails.
- Media attorney Douglas J. Wood notes that consumers are legally liable for unauthorized spending by AI agents, as card issuers view the agent as an authorized user, leaving users without loss protection.
- Axios testing found that while Muse and Dots excel at research and planning, they struggle with completing purchases, often getting stuck at sign-in pages or requiring manual user intervention.
Background
Since September 2026, major tech firms have launched personal AI agents capable of handling everyday tasks, sparking a debate over security and privacy. Earlier coverage highlighted concerns about rogue behavior, unauthorized actions, and privacy risks, with industry leaders urging users to limit access and require human approval for sensitive tasks. The rapid adoption of these tools, particularly Meta's Muse, has raised questions about long-term user retention and the balance between convenience and control.
How outlets are covering it
CBS News emphasizes the security risks of personal AI agents, citing experts like Hed Kovetz and Lynette Owens who warn against granting full access to sensitive data due to insufficient security measures and the threat of prompt injection attacks. In contrast, entrepreneur Chris Franco argues that the benefits of AI agents outweigh the risks, comparing data sharing to previous ad platform practices and emphasizing the need for strict instructions and monitoring. Rest of World focuses on the global implications of AI agents, highlighting challenges in non-English languages, cultural nuances, and internet connectivity in developing nations, which may widen the digital divide. The Economic Times provides a practical perspective, illustrating how AI agents can handle complex tasks like managing flight payments and subscriptions, but stresses the need for users to balance convenience with control. Axios testing highlights the current limitations of AI agents in completing purchases, noting that while they excel at research and planning, they often struggle with automated transactions, requiring manual user intervention. These perspectives collectively underscore the ongoing debate over the trade-off between the convenience of AI agents and the risks they pose to security, privacy, and global equity.
Why it matters
The rise of personal AI agents like Meta's Muse and OpenAI's Dots marks a significant shift in how consumers interact with technology, offering unprecedented convenience but also introducing new risks. As these tools become more prevalent, understanding their capabilities and limitations is crucial for making informed decisions about their use. The security and privacy concerns highlighted by experts, along with the global implications of their deployment, underscore the need for robust safeguards and regulatory frameworks to ensure that AI agents benefit users without compromising their safety or equity. This debate will shape the future of AI integration in everyday life, influencing how we balance innovation with protection.
What to watch
As personal AI agents continue to evolve, expect increased scrutiny from regulators and cybersecurity experts to address security vulnerabilities and privacy concerns. Users may see more sophisticated safeguards and transparency tools, such as plain-language summaries of agent actions, to enhance trust and control. The global expansion of AI agents will likely face challenges related to language support, cultural nuances, and internet connectivity, potentially widening the digital divide. Additionally, the legal landscape may evolve to clarify liability for unauthorized actions by AI agents, with potential changes in consumer protection laws. As AI agents become more integrated into daily life, the balance between convenience and control will remain a critical focus, with users and developers working to find the optimal level of autonomy for these tools.
- Should you trust personal AI agents with your money and data? Here's what experts say. CBS News
- Will developing nations be able to handle millions of AI agents? Rest of World
- Personal AI agents can now act. How much should we let them do? The Economic Times
- I let agents plan a WNBA Finals trip (but kept my wallet to myself) Axios
- Main Street Ledger: Agentic AI Is Here. The Rules of the Road Must Keep Pace. consumerbankers.com
Want the full story? Read the original reporting
Read on CBS News