
Public PoC Unleashes Windows 'MiniPlasma' Privilege-Escalation to SYSTEM
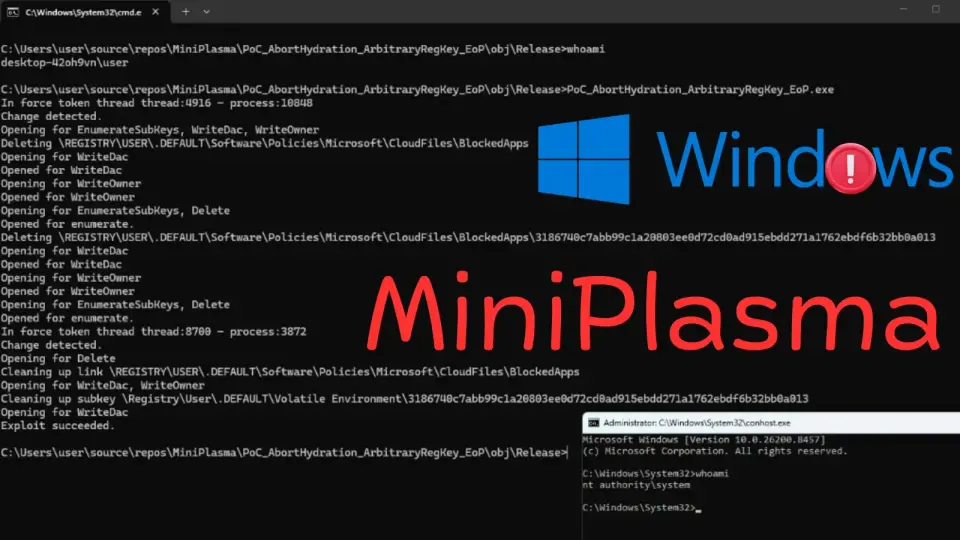
TL;DR
A publicly released PoC for the Windows 'MiniPlasma' zero-day privilege-escalation flaw lets unprivileged users gain SYSTEM privileges by exploiting the Cloud Filter driver’s HsmOsBlockPlaceholderAccess race condition and writing to the .DEFAULT hive. The bug traces to CVE-2020-17103 (originally patched in 2020 by Microsoft) but the PoC shows the flaw remains exploitable; Nightmare-Eclipse released the exploit on GitHub on May 13, 2026, after May Patch Tuesday, increasing risk as weaponized code circulates and affects all Windows versions. Organizations should monitor Microsoft’s response and apply patches when available.
Topics:technologycyber-security-news#cyber-security-news#miniplasma#nightmare-eclipse#privilege-escalation#windows#zero-day
- New Windows 'MiniPlasma' Zero-Day Let Attackers Gain SYSTEM Access - PoC Released CyberSecurityNews
- MiniPlasma Windows 0-Day Enables SYSTEM Privilege Escalation on Fully Patched Systems The Hacker News
- BitLocker zero-day exposes Windows drives as PoC goes public Bitdefender
- Zero-day exploit completely defeats default Windows 11 BitLocker protections Ars Technica
- A new Windows 11 BitLocker bypass only needs a USB stick, and the researcher thinks it's a backdoor XDA
Want the full story? Read the original reporting
Read on CyberSecurityNews