
"CISA Urges Immediate Action to Patch Exploited Microsoft SharePoint Vulnerability"
TL;DR
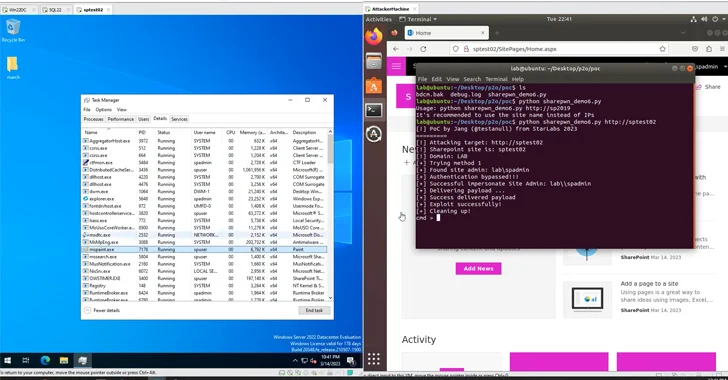
CISA has identified an actively exploited critical security vulnerability in Microsoft SharePoint Server, allowing attackers to gain administrator privileges. The vulnerability, CVE-2023-29357, was demonstrated at a hacking contest and combines authentication bypass with a code injection bug. Federal agencies are urged to apply patches by January 31, 2024, to protect against this threat.
Topics:technologycybersecurity#cisa#cve-2023-29357#cyber-attack#cybersecurity#microsoft-sharepoint#vulnerability
Want the full story? Read the original reporting
Read on The Hacker News