
Entra Agent ID Flaw Lets Attackers Seize Privileged Service Principals
TL;DR
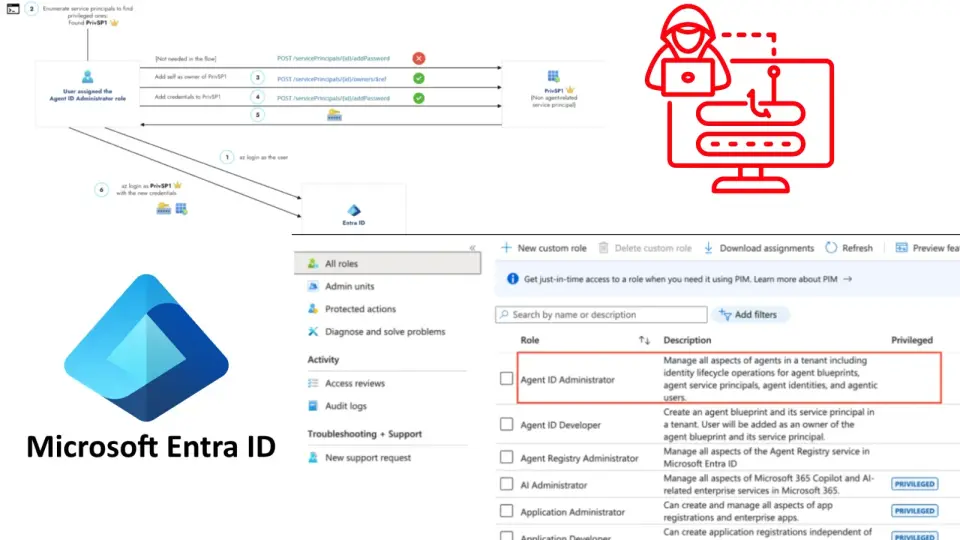
A critical flaw in Microsoft Entra’s Agent Identity Platform allowed users with the Agent ID Administrator role to take ownership of any service principal, generate new credentials, and impersonate high-privilege apps, enabling tenant-wide compromise; Microsoft patched the issue across cloud environments by April 2026. Security teams should identify and secure privileged service principals, using Azure CLI and the Microsoft Graph API to audit configurations and prevent abuse.
Topics:technologycybersecurity#cybersecurity#entra#microsoft-entra#privilege-escalation#service-principal#silverfort
- Hackers Can Abuse Entra Agent ID Administrator Role to Hijack Service Principals CyberSecurityNews
- Azure SRE Agent flaw lets outsiders silently eavesdrop on enterprise cloud operations csoonline.com
- Hackers Exploit Agent ID Administrator Role to Hijack Service Principals gbhackers.com
- Hackers Can Abuse Agent ID Administrator Role to Hijack Service Principals cyberpress.org
Want the full story? Read the original reporting
Read on CyberSecurityNews