
Beware: Android Malware Stealing WhatsApp Backups and Chats
TL;DR
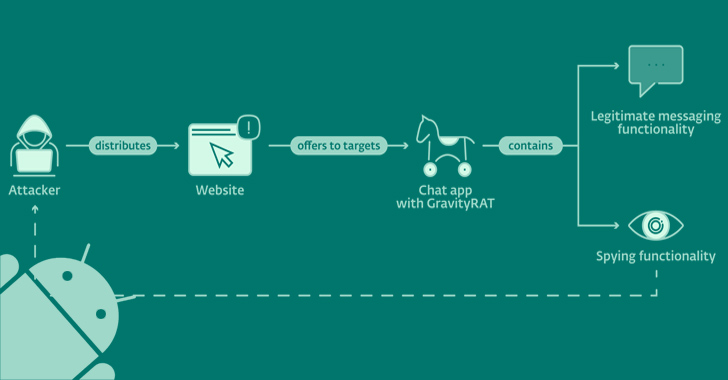
GravityRAT, a cross-platform malware capable of targeting Windows, Android, and macOS devices, has been found masquerading as messaging apps BingeChat and Chatico in a narrowly targeted campaign since June 2022. The updated version of the Android remote access trojan can exfiltrate WhatsApp backups and receive commands to delete files. The threat actor is suspected to be based in Pakistan, with recent attacks involving GravityRAT targeting military personnel in India and among the Pakistan Air Force by camouflaging it as cloud storage and entertainment apps.
Topics:technologymobile-security-privacy#android-trojan#backups#gravityrat#malware#mobile-security-privacy#whatsapp
- Warning: GravityRAT Android Trojan Steals WhatsApp Backups and Deletes Files The Hacker News
- Android GravityRAT malware now steals your WhatsApp backups BleepingComputer
- Free chat apps were caught stealing users' WhatsApp data — delete them before you're next Laptop Mag
- Android GravityRAT goes after WhatsApp backups We Live Security
- Android apps could be stealing your private WhatsApp chats - delete them now The Mirror
- View Full Coverage on Google News
Want the full story? Read the original reporting
Read on The Hacker News