
"Critical Flaw in TP-Link C5400X Router Exposes Gamers to Remote Attacks"
TL;DR
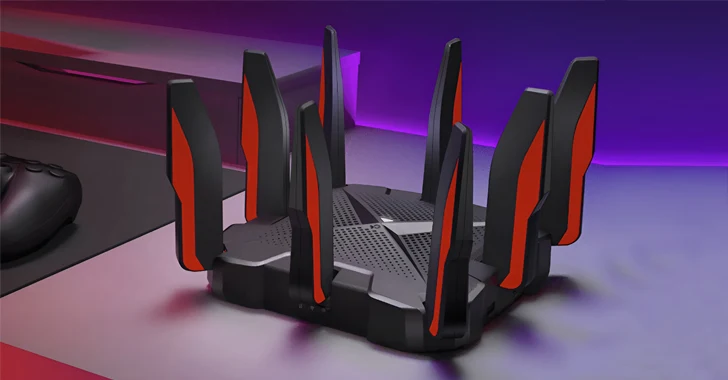
A critical security flaw in the TP-Link Archer C5400X gaming router, tracked as CVE-2024-5035, allows remote code execution via specially crafted requests. The vulnerability, with a CVSS score of 10.0, affects all firmware versions up to 1_1.1.6 and has been patched in version 1_1.1.7. The flaw is linked to the "rftest" binary, which can be exploited by injecting commands after shell meta-characters. Users are advised to update to the latest firmware to mitigate the risk.
Topics:technologyvulnerability-network-security#cybersecurity#firmware-update#remote-code-execution#security-flaw#tp-link#vulnerability-network-security
- TP-Link Gaming Router Vulnerability Exposes Users to Remote Code Attacks The Hacker News
- TP-Link fixes critical RCE bug in popular C5400X gaming router BleepingComputer
- TP-Link Archer C5400X gaming router is affected by a critical flaw Security Affairs
- TP-Link Archer C5400X Vulnerability Exposes Gamers Online The Cyber Express
Want the full story? Read the original reporting
Read on The Hacker News