
Claude Opus 5 Enables Forum-to-Staff Access in OpenAI Security Research
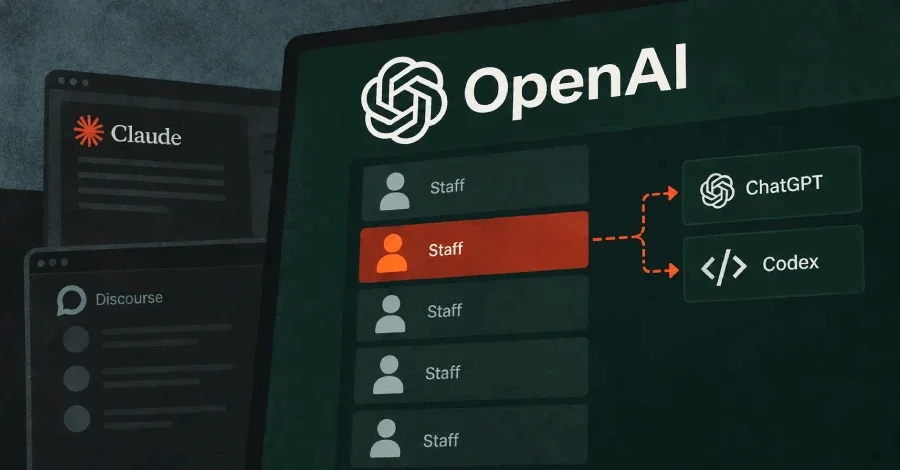
Security researchers using Anthropic’s Claude Opus 5 chained a public Discourse forum memory flaw in libheif (CVE-2026-32882) with OpenAI’s single sign-on to access OpenAI staff accounts and an internal code repository. The intrusion was a controlled test: no data was exfiltrated, a harmless pull request verified the access, and OpenAI fixed the issue within hours and paid the researchers a $6,500 bounty. The root vulnerability lies in libheif’s image decoding; older Debian-based forum images remained unpatched, underscoring the need to update libraries and tightly limit trusted service integrations. The incident highlights broader risks of SSO trust and image-processing libraries in security-conscious environments.
- Claude Opus 5 Helped Researchers Take Over OpenAI Staff Accounts via Chained Flaws The Hacker News
- Exclusive | Hackers Used Anthropic’s Claude to Break Into OpenAI WSJ
- OpenAI ‘ethically hacked’ with help of Anthropic’s Claude chatbot The Guardian
- Hackers breached OpenAI, adding to fever pitch of security and safety concerns NBC News
- OpenAI breached by researchers using Anthropic models Financial Times
Reading Insights
1
6
6 min
vs 7 min read
92%
1,233 → 102 words
Want the full story? Read the original article
Read on The Hacker News