
GMO Internet Launches $1M Bounty to Identify Hackers Behind FX Cloud Breach
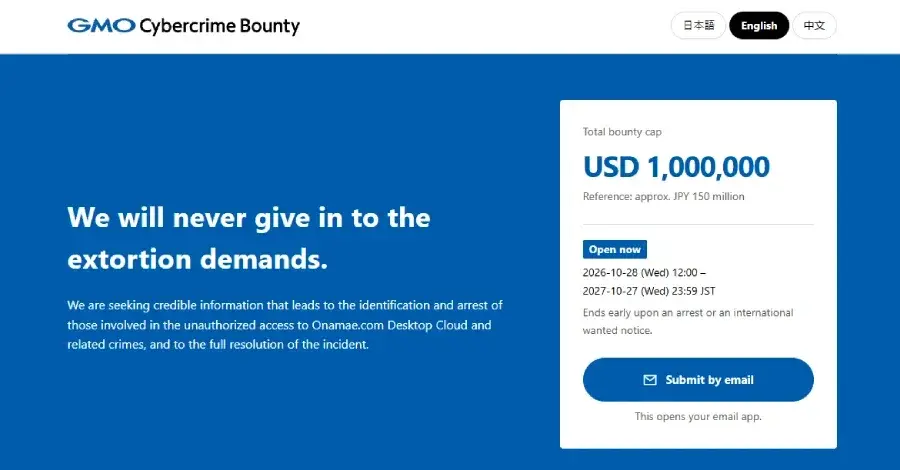
Japanese ISP GMO Internet Group has launched a $1 million bounty program to identify attackers who breached its Onamae.com Desktop Cloud service, which hosts Windows desktops for foreign exchange (FX) trading. The company refused a $50 million ransom demand and is offering rewards only for tips leading to arrests or international wanted notices. The breach, discovered on October 20, potentially affected 26,739 servers, leading to unauthorized trades on customer accounts via leaked credentials. GMO has compensated users with cash and is covering confirmed trading losses, while urging customers to change passwords and enable two-factor authentication.
Key points
- GMO Internet Group offers up to $1 million for tips leading to the arrest of hackers or an Interpol Red Notice, with the program running until October 27, 2027, or until a successful outcome.
- The breach of the Onamae.com Desktop Cloud service potentially affected 26,739 servers, with confirmed exfiltration of customer information and unauthorized access to FX trading accounts.
- Attackers demanded approximately $50 million (¥8 billion) on October 21 and posted customer data on their website on October 27, though no ransomware attack was confirmed by that time.
- GMO Internet is compensating current users with ¥5,000 and covering confirmed unauthorized trading losses, while offering a six-month free migration to a separate service for those who wish to leave the breached platform.
- CEO Masatoshi Kumagai admitted that internal white-hat hackers had warned the team about security flaws, but the response was too slow, allowing attackers to exploit the gap.
Background
This incident follows a pattern of high-profile breaches in 2026, including the Asos data compromise in October and AI-assisted breaches at OpenAI in September. GMO’s response highlights the growing trend of companies using financial incentives to combat cybercrime when traditional law enforcement is slow. The breach also underscores the risks of shared administrator accounts and default visibility of customer drives in cloud-based VPS environments, as claimed by the attackers.
Why it matters
The GMO breach illustrates the severe financial and operational risks associated with cloud-based trading platforms. By refusing to pay the ransom and instead offering a bounty, GMO sets a precedent for corporate response to extortion. The incident also highlights the critical importance of strong authentication and the dangers of shared credentials in enterprise environments, as leaked logins led to real-world financial losses for customers.
What to watch
GMO will continue to accept tips until an arrest is made or October 27, 2027. The company plans to provide details on the free alternative service by October 30 and will continue analyzing customer PCs for malware. Customers are advised to monitor their trading accounts and change passwords from secure devices.
Want the full story? Read the original reporting
Read on The Hacker News