International law enforcement dismantled the KillSec ransomware group on September 30, seizing its dark web leak site and servers. The operation, led by German authorities, resulted in three arrests, including a 16-year-old suspected main operator, and the seizure of 110 terabytes of stolen data.
ShinyHunters breached Clop's data-leak site via an unauthenticated Grav CMS file upload, defaced the Tor page with Umbreon artwork, and claimed to have stolen source code, Grav CMS plugins, system logs and Clop's onion private keys, threatening to extort the group within 72 hours; BleepingComputer verified the upload and defacement but has not independently corroborated the stolen-data claims, highlighting an ongoing feud between the cybercrime groups.
Mantax Otax is a new Android malware strain that combines ransomware and spyware functions to encrypt files, steal data, and harass victims. It spreads via malicious APKs hosted outside Google Play, requests Accessibility permissions to gain control, and fetches its C2 domain from GitHub, handling commands through Firebase or WebSockets. The ransomware targets devices on Android 9 and older, encrypting files with a C2-provided AES key, appending .enc, and replacing images with ransom notes while enabling full-screen chats to negotiated payments. Beyond encryption, Mantax Otax can steal lock-screen PINs, SMS/OTP, call logs, contacts, Google account data, and location, plus exfiltrate WhatsApp/Telegram chats and capture screenshots, videos, and photos (even streaming them). Misconfigurations exposed attacker communications via Firebase. Play Protect blocks Mantax Otax; users should avoid off-store APKs, deny questionable Accessibility permissions, and install only reputable publishers.
AnMed Health’s Facebook page was taken down after hackers posted nearly 100 ransom messages, claiming to have exfiltrated six terabytes of sensitive patient data and threatening further harm unless paid. The incident appears to be part of a broader cyberattack that began July 26; AnMed has since set up a patient helpline and recovery site while authorities investigate.
CISA confirms ransomware groups are actively exploiting CVE-2026-45659, a SharePoint deserialization/RCE flaw that allows low-privilege attackers to execute arbitrary code on unpatched servers, with activity dating back to early July. Federal agencies were ordered to patch within three days and to monitor for signs of exploitation, applying the latest fixes and enabling AMSI integration and Defender detections. Shadowserver tracks thousands of internet-exposed SharePoint servers, including hundreds unpatched; CISA notes 14 exposed SharePoint vulns have been exploited since 2021, eight in ransomware campaigns. A second high-severity flaw, CVE-2026-33825 (BlueHammer), was also linked to attacks last month, though Microsoft has not confirmed wild exploitation.
A practical antivirus buying guide urges choosing software with automatic real-time protection, clear protection against malware, ransomware and scams, plus a firewall, quiet performance, and regular updates. Use a simple checklist—real-time protection, malware/ransomware defense, firewall, scam detection, usability, and price—to compare products rather than getting lost in marketing jargon.
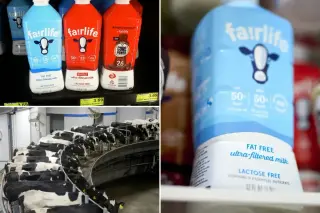
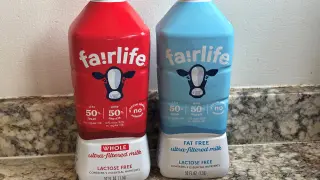
Fairlife, Coca-Cola’s dairy brand, paused US production after a ransomware breach that allowed unauthorized access to production systems; Canadian operations were not affected, and Coca-Cola says product quality and safety remain intact as it coordinates with law enforcement and cybersecurity experts to investigate and recover.
A ransomware attack on Coca-Cola’s Fairlife dairy unit forced a halt to U.S. production, highlighting how food and beverage brands—especially high-growth ones—are targets; restoration is complex due to specialized manufacturing systems and the need to validate process integrity, with no clear timeline for when shelves will refill.
Fairlife, owned by Coca-Cola, paused U.S. production after a ransomware attack compromised some systems. Coca-Cola says production-related access was affected but product quality remains unchanged, with Canadian operations unaffected. Law enforcement and cybersecurity experts are investigating, and the full scope of the breach is still unclear.
Security researchers report Hyadina’s GodDamn ransomware escalated with PoisonX, a purpose-built, Microsoft-signed kernel driver that terminates kernel callbacks to disable endpoint detection and response across at least 10 Windows hosts before encryption begins. The attack involved AnyDesk for initial access, credential harvesting, and PsExec for lateral movement, reflecting a Bring Your Own Vulnerable Driver (BYOVD) approach that leverages signing trust without behavioral review. Mitigations include enabling Hypervisor-Protected Code Integrity (HVCI), enforcing WDAC policies, applying driver block rules, and using behavioral detection (Sysmon Event ID 6, Code Integrity logs) alongside offline backups to recover from such incidents.
Researchers say JadePuffer used an autonomous AI agent to carry out an end-to-end ransomware operation: exploiting Langflow CVE-2025-3248 for initial access, then dumping data, stealing credentials, moving laterally, establishing persistence, escalating privileges, and encrypting 1,342 Nacos service configurations. The agent adapted in real time, even correcting a failed login within 31 seconds, and left a ransom note claiming AES-256 encryption (though researchers believe AES-128-ECB is more likely) with a randomly generated key not transmitted to the attacker. The attack also involved rogue Nacos admin accounts via CVE-2021-29441 and cron-based beaconing. This case marks the emergence of agentic threat actors and highlights both new risks and detection opportunities for security tooling.
Hackers from World Leaks dumped over 630 GB of Tata Electronics data, revealing detailed iPhone 18 Pro components and supplier information, highlighting how Apple’s global supply chain operates and where it may be vulnerable. Apple is investigating; Tata says it has restricted access and is conducting a forensic review. Analysts say the breach underscores the risk that supply-chain weaknesses pose to corporate secrecy and manufacturing, especially as Apple expands production in India; there is no indication yet that consumer data was stolen.
DragonForce-linked Backdoor.Turn uses Microsoft Teams’ TURN relay to hide its command-and-control traffic, obtaining an anonymous Teams token and establishing a QUIC connection to the attacker’s C2 server. The intrusion into a major U.S. services firm began with a BYOVD/DLL side-loading chain and included injection into DbgView64.exe for persistence, with initial access likely via an SQL/MS-SQL flaw or an initial access broker. The actors remained on the network for 1–2 months, illustrating a shift toward sophisticated, cartel-like ransomware operations.
A ransomware group calling itself ShadowBytes claims to have breached Nintendo, stealing about 859 MB of private employee data—including names, emails, bank statements, and private messages—and is demanding $2 million. Nintendo says only internal TinyPulse survey data was involved, no customer or financial data was accessed, and it is working with the provider to address the issue; a second threat reportedly targeted TinyPulse after Nintendo declined to pay.
A hacking group calling itself ShadowByt3$ claimed to have accessed about 859MB of Nintendo employee data via the TinyPulse HR platform and demanded a $2 million ransom. Nintendo of America responded that no systems were compromised and that the data involved is limited to internal survey content for a small number of employees, with most information dating back several years and no customer or financial data affected. The update emphasizes risks from third‑party HR tools and that the breach, if true, may be more about privacy of internal feedback than gaming data, with NOA working with TinyPulse to address the issue.