
MacStealer Malware Steals Apple User Data and Passwords
TL;DR
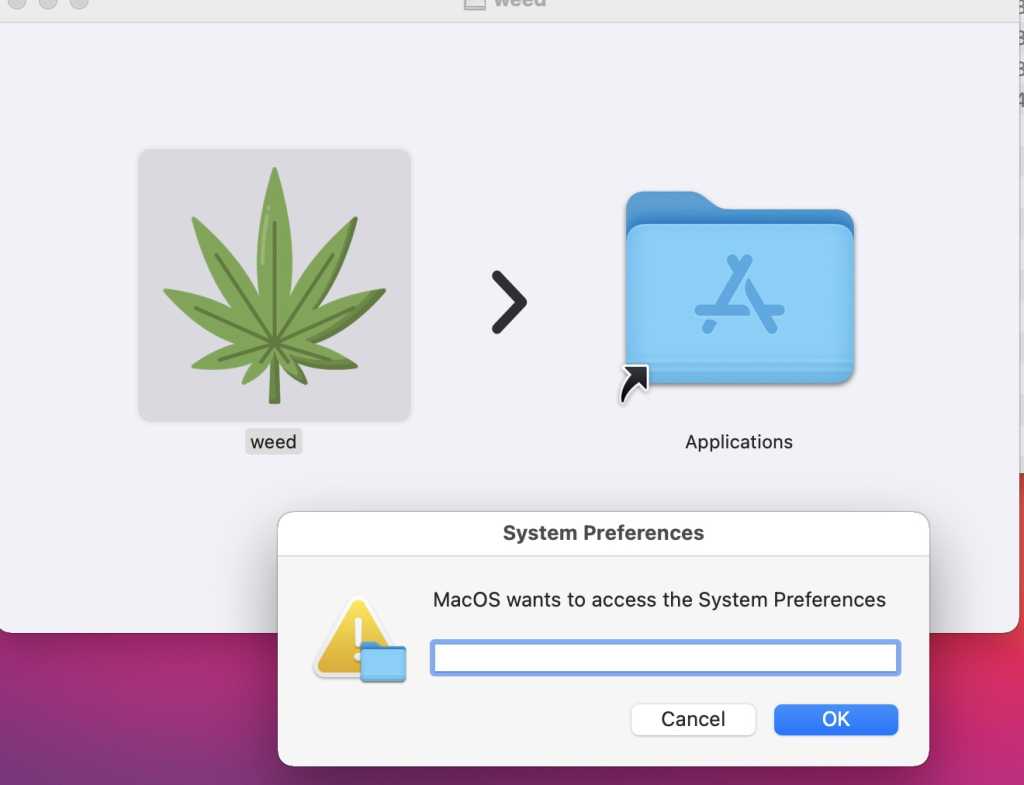
MacStealer malware can attack Macs running macOS Catalina or later, with either Intel or Apple M-series chips. It can get passwords, cookies, and credit card data from Firefox, Google Chrome, and Microsoft Brave browsers, and extract several different file types, including .txt, .doc, .jpg, and .zip, and it can extract the KeyChain database. MacStealer appears to propagate through a “weed.dmg” executable file. It’s unclear if MacStealer has been logged in the CVE.report database that tracks vulnerabilities and exposures, and Apple has not commented on the malware.
- Scary 'MacStealer' malware goes after iCloud passwords and credit card data Macworld
- MacStealer malware grabs passwords, files, and credit card details 9to5Mac
- New MacStealer macOS malware steals passwords from iCloud Keychain BleepingComputer
- MacStealer Malware Plucks Bushels of Data From Apple Users Dark Reading
- New malware steals Mac passwords & sends them with Telegram AppleInsider
- View Full Coverage on Google News
Want the full story? Read the original reporting
Read on Macworld