
Massive Laravel-Lang Breach Sparks Cross-Platform Credential Theft
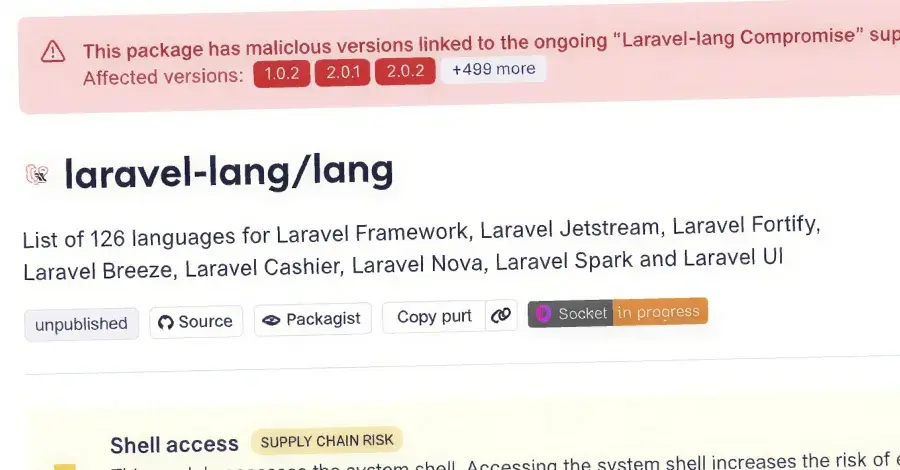
Security researchers warn of a broad compromise of Laravel-Lang PHP packages (laravel-lang/lang, http-statuses, attributes, actions) that injected a malicious src/helpers.php into autoloaded vendor files. The attack involved rapid tagging of 700+ package versions in May 2026, suggesting access to the Laravel Lang release infrastructure. The embedded dropper runs on startup and delivers a ~5,900-line PHP credential stealer that exfiltrates cloud tokens, service credentials, browser data, VPN configs and more to flipboxstudio.info, encrypts results with AES-256, and self-deletes. Windows uses a Visual Basic Script launcher; Linux/macOS execute the payload via shell. Remediation includes auditing dependencies, rotating credentials, upgrading to clean versions, and monitoring for indicators of compromise.
- Laravel-Lang PHP Packages Compromised to Deliver Cross-Platform Credential Stealer The Hacker News
- Supply Chain Attack Targets Laravel-Lang Packages with Credential Stealer Aikido Security
- Laravel-Lang Supply Chain Attack: Every Tag Across Multiple Composer Packages Rewritten to Steal CI Secrets StepSecurity
- Hackers Compromised 233 Versions of Laravel-Lang Packages by Hacking 700 GitHub Repos CyberSecurityNews
- Laravel Lang Supply Chain Advisory Snyk
Want the full story? Read the original reporting
Read on The Hacker News