
Major React Native Security Flaws Endanger Millions of Developers
TL;DR
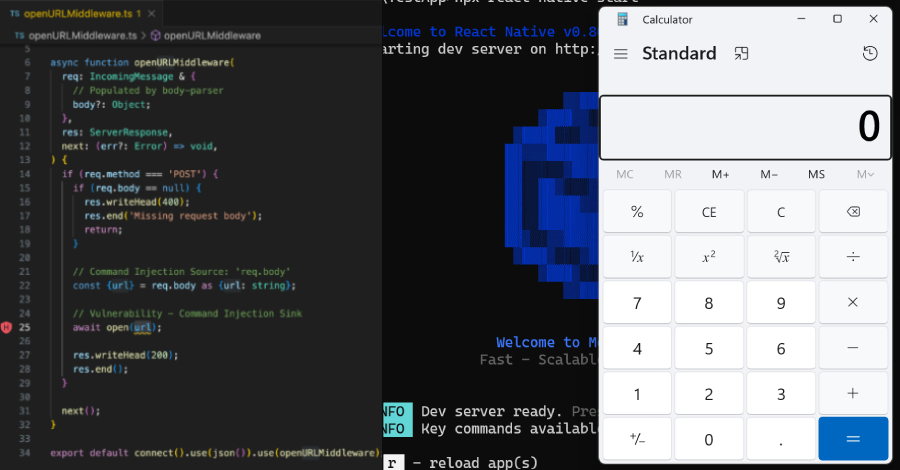
A critical security vulnerability in the '@react-native-community/cli' npm package, affecting millions of developers, allowed remote attackers to execute arbitrary OS commands via the Metro development server. The flaw, tracked as CVE-2025-11953 with a CVSS score of 9.8, has been patched in version 20.0.0, highlighting the importance of security scanning in the software supply chain.
Topics:technologysecurity#cve-2025-11953#react-native#remote-attack#security#security-flaw#supply-chain-security
- Critical React Native CLI Flaw Exposed Millions of Developers to Remote Attacks The Hacker News
- Critical Flaw in Popular React Native NPM Package Exposes Developers to Attacks SecurityWeek
- JFrog discloses CVSS 9.8 React vulnerability putting millions of developers at risk SiliconANGLE
- Severe RCE Flaw in Widely Used React Native NPM Library Puts Developers at Risk Cyber Press
- Critical RCE Vulnerability in Popular React Native NPM Package Exposes Developers to Attacks CyberSecurityNews
Want the full story? Read the original reporting
Read on The Hacker News