
Rovo Flaw Lets Attackers Exfiltrate Jira/Confluence Data via Prompt Injection
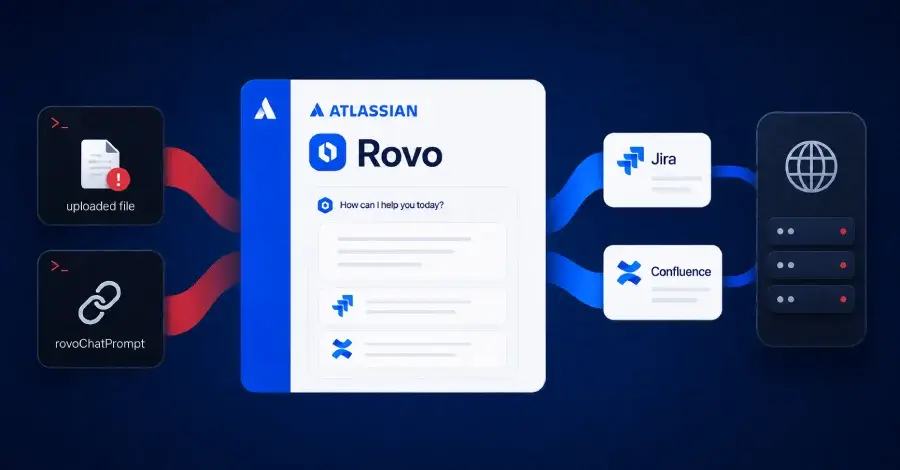
Security researchers found that Atlassian's Rovo assistant can be tricked into sending Jira and Confluence data to attackers through attacker-controlled prompts and a malicious URL parameter. Two independent reports (PromptArmor and Varonis Threat Labs) detail a content-borne prompt injection path and a one-click link path, with Atlassian fixing the link-based flaw on July 8, 2026; the content-borne path’s status remained uncertain as of Aug 8, 2026. Exfiltration occurs within the victim’s signed-in permissions, and admins can mitigate by restricting Rovo usage by app/group or disabling Rovo features. No CVEs have been issued. Organizations should tighten app scopes and permissions rather than relying on the web-search toggle as a security boundary.
- Atlassian Rovo Can Be Tricked Into Sending Jira and Confluence Data to Attackers The Hacker News
- Critical One-Click Vulnerability in Atlassian’s Rovo AI Exposed Enterprise Data SecurityWeek
- RovoBlast: How One Click Triggered Atlassian’s AI Assistant to Leak Data HackerNoon
- A vulnerability has been discovered in Atlassian's AI 'Rovo' that allows internal company data to be transmitted externally simply by having it read documents. GIGAZINE
Want the full story? Read the original reporting
Read on The Hacker News