Tag

Apple Security

All articles tagged with #apple security

Mac Vulnerability Exploitation and Apple’s Tightening Grip on AI Agents
technology5 days ago

Mac Vulnerability Exploitation and Apple’s Tightening Grip on AI Agents

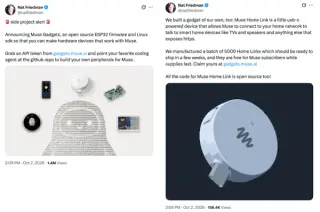
A high-severity macOS vulnerability, CVE-2026-65400, is under active exploitation, allowing attackers to gain root access via exposed screen-sharing ports. While Apple patched the flaw, the incident highlights friction between AI agents and macOS security controls. Ben Thompson argues that Apple’s restrictive permissions and delayed smart-home strategy clash with the emerging reality of autonomous agents, which may render traditional app-based ecosystems obsolete.
Proof-of-Concept Reveals How Malicious PDFs Trigger Apple CoreGraphics Crash
security8 days ago

Proof-of-Concept Reveals How Malicious PDFs Trigger Apple CoreGraphics Crash

Security researchers have released a proof-of-concept for CVE-2026-86950, an Apple CoreGraphics flaw patched on September 28. The vulnerability, triggered by a malicious PDF with a crafted font, causes a crash on unpatched iOS and macOS devices. While Apple confirmed the flaw was used in targeted attacks, the new analysis demonstrates only a memory corruption crash, not full code execution. CISA mandated federal agencies patch by October 2, and researchers noted potential links to WhatsApp delivery mechanisms, though Meta has not confirmed involvement.

Apple Urges Immediate Updates to Patch Actively Exploited Zero-Day in CoreGraphics
technology10 days ago

Apple Urges Immediate Updates to Patch Actively Exploited Zero-Day in CoreGraphics

Apple released emergency updates for iPhones, iPads, and Macs to patch a critical zero-day vulnerability (CVE-2026-86950) in the CoreGraphics framework. This out-of-bounds write flaw allows arbitrary code execution and is being actively exploited in highly targeted attacks against users of iOS versions prior to iOS 27. While the attacks appear sophisticated and limited to specific individuals, security experts urge all users to update immediately to mitigate risks, as the vulnerability affects devices back to the iPhone 11. CISA has also mandated federal agencies to patch within three days.

Apple ships macOS 27.0.1 and security patches for Tahoe and Sequoia
technology11 days ago

Apple ships macOS 27.0.1 and security patches for Tahoe and Sequoia

Apple released macOS 27.0.1 Golden Gate, macOS 26.7.1 Tahoe, and macOS 15.8.1 Sequoia on September 28, 2026. The update follows two release candidates and addresses security vulnerabilities, including a CoreGraphics flaw in older versions. macOS 27.0.1 contains no published CVEs, while Tahoe and Sequoia fix an out-of-bounds write issue. The release marks the first update for the new Golden Gate OS, which supports only Apple Silicon Macs.

"iOS 17.3: Strengthening iPhone Security and Introducing Exciting Features"
technology2 years ago

"iOS 17.3: Strengthening iPhone Security and Introducing Exciting Features"

With the release of iOS 17.3, Apple aims to address the iPhone theft problem by introducing a Stolen Device Protection feature. The Wall Street Journal's Joanna Stern interviewed a prolific iPhone thief who exploited the iOS vulnerability to make over $20,000 every weekend. The thief would observe victims entering their passcodes, then steal their iPhones and change the Apple ID password to gain access to banking apps and personal information. Bars were the preferred target location, with college-age men being the ideal victims. The thief would erase the stolen iPhones and sell them overseas, making a significant profit. The criminal has since been sentenced to 94 months in jail.