
ClickFix Campaign Uses Fake Blue Screens to Infect Hotels with Malware
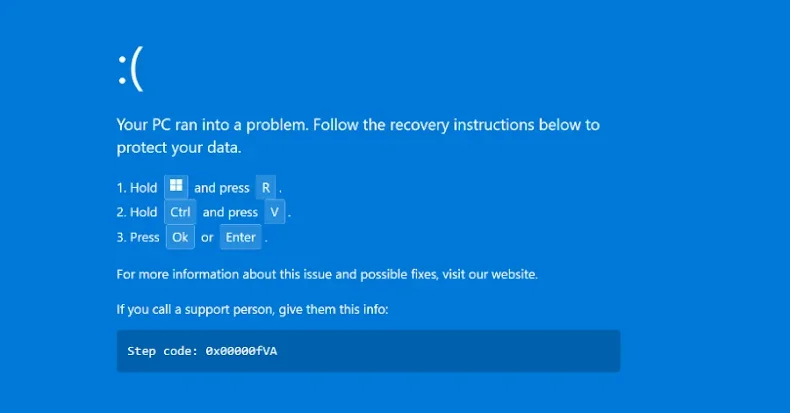
TL;DR
Cybersecurity researchers have uncovered a campaign targeting European hospitality staff using fake booking cancellation emails and BSoD pages to deliver the DCRat remote access trojan, employing sophisticated techniques like living-off-the-land methods and malware evasion tactics.
Topics:technologycybersecurity#bsod#cybersecurity#dcrat#endpoint-security#european-hospitality#phishing
- Fake Booking Emails Redirect Hotel Staff to Fake BSoD Pages Delivering DCRat The Hacker News
- Hotel staff tricked into installing malware by bogus BSODs theregister.com
- ClickFix attack uses fake Windows BSOD screens to push malware BleepingComputer
- ClickFix Campaign Serves Up Fake Blue Screen of Death Dark Reading
- ClickFix Malware plays havoc on European Hotels and overall hospitality industry Cybersecurity Insiders
Want the full story? Read the original reporting
Read on The Hacker News