Tag

Phishing

All articles tagged with #phishing

Attackers Weaponize ChatGPT Custom GPTs to Deploy RATs via ClickFix
cybersecurity9 days ago

Attackers Weaponize ChatGPT Custom GPTs to Deploy RATs via ClickFix

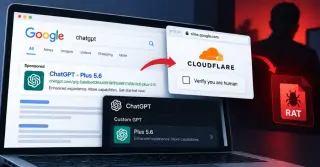
Threat actors are abusing ChatGPT Custom GPTs to deliver remote access trojans (RATs) through ClickFix lures. Huntress identified a campaign where malicious GPTs, hosted on the legitimate chatgpt.com domain, redirect users to fake Cloudflare CAPTCHA pages. These pages trick victims into executing PowerShell commands that install malware. The infection chain uses signed binaries to sideload malicious DLLs, ultimately deploying a RAT capable of data theft, surveillance, and network persistence. At least 40 users have been infected, with the initial entry point often being sponsored Google ads for 'chatgpt'.
Star Blizzard shifts to automated RedFlick attacks against Ukraine-linked targets
cybersecurity9 days ago

Star Blizzard shifts to automated RedFlick attacks against Ukraine-linked targets

Russian state actor Star Blizzard has adopted a new malware delivery method called RedFlick to automate the installation of the CosmicPulse backdoor. This technique reduces the need for manual victim interaction compared to previous ClickFix campaigns. Microsoft reports that at least 13 large-scale phishing campaigns have impacted over 100 organizations, primarily in the US and UK, since January 2026.

Microsoft Dismantles AI‑Driven Scam That Breached 12,000 Accounts
technology18 days ago

Microsoft Dismantles AI‑Driven Scam That Breached 12,000 Accounts

Microsoft led an industry-wide takedown of EvilTokens, an AI-assisted platform that automated mass email compromises, using a device-code OAuth workflow to hijack Microsoft accounts and identify high‑value targets. The service compromised about 12,000 accounts across 10,000 organizations before authorities seized 50 sites and 150 domains and the UK arrested two men. The incident underscores the need for strong identity protections and independent verification of payment-change requests.

Homoglyph alert: how fake URLs fool you and how to stay safe
technology20 days ago

Homoglyph alert: how fake URLs fool you and how to stay safe

Fraudsters are increasingly using homoglyphs—look-alike characters from different alphabets (like Cyrillic letters) in URLs and emails—to fool people into clicking fake links. Most phishing now relies on spoofed URLs rather than attachments; to defend, type known addresses manually, verify links by visiting the official site, keep your browser updated, enable 2FA/MFA, and report any suspected fraud or compromised credentials.

Passkey phishing surge targets Microsoft 365 data in extortion-linked campaign
technology28 days ago

Passkey phishing surge targets Microsoft 365 data in extortion-linked campaign

Microsoft warns that extortion-linked groups are using passkey- and SSO-themed social engineering (AiTM and device-code phishing) to compromise Microsoft 365 accounts, perform reconnaissance with Microsoft Graph, and exfiltrate data from SharePoint Online and OneDrive over hours to days, often registering convincing phishing domains and adding attacker-controlled authentication methods; defenders should deploy phishing-resistant MFA, revoke sessions, reset credentials, remove attacker-added methods, and restrict sensitive cloud resources to managed devices.

Executive Vishing Campaign Cracks Microsoft 365 with MFA Token Theft
technology1 month ago

Executive Vishing Campaign Cracks Microsoft 365 with MFA Token Theft

Threat actors impersonating IT desk staff use vishing and an adversary-in-the-middle token theft flow to harvest Microsoft 365 credentials and MFA approvals, enabling access to authenticated sessions via proxy replay; they exfiltrate data from SharePoint, OneDrive, Exchange, and Box, targeting executives across sectors. Defenses include phishing-resistant MFA, Conditional Access, restricting SharePoint data access, and employee training on vishing risks.

Invisible Unicode Tricks Power Large-Scale Phishing Campaign
technology1 month ago

Invisible Unicode Tricks Power Large-Scale Phishing Campaign

Microsoft warns of a large-scale phishing campaign that hides messages by embedding invisible Unicode characters (ASCII smuggling) in finance-related words to evade filters; peak volume reached about 2.37 million daily messages in February and persisted into May; the campaign used ActiveCampaign infrastructure and was detected by Defender using other signals; defenders should normalize Unicode tag characters before detection and even before feeding content to AI to curb prompt-injection risks.

Phishing Goes Incognito: Invisible Unicode Tricks Evade Filters
technology1 month ago

Phishing Goes Incognito: Invisible Unicode Tricks Evade Filters

Microsoft uncovered a massive phishing campaign that used invisible Unicode tag characters to hide content and split keywords, a form of ASCII smuggling that can bypass filters and extend beyond AI prompts into traditional email scams. The campaign peaked at 2.37 million messages in late February from finance-themed domains with weekday bursts and weekend lulls, and declined thereafter. Defenders are advised to normalize/tokenize to strip non-rendering Unicode points and monitor behavioral patterns like weekday-on/weekend-off activity.

TerminalFix lurks behind fake CAPTCHAs to deliver a stealth reverse-tunnel backdoor
technology1 month ago

TerminalFix lurks behind fake CAPTCHAs to deliver a stealth reverse-tunnel backdoor

Microsoft warns of TerminalFix, a new ClickFix variant that uses fake Cloudflare CAPTCHA prompts to coax victims into running PowerShell in Windows Terminal, then downloads a signed executable and a malicious DLL, with payloads hidden in PNG images via steganography. The malware establishes persistence, conducts AD/network reconnaissance, and employs a custom Python reverse-tunnel over an encrypted WebSocket to reach internal hosts, enabling attacker control and potential lateral movement, data theft, or ransomware. Defenses include restricting/logging PowerShell, monitoring for LockScreenContentServer.exe, hardening browsers/endpoint protections, and rotating credentials if compromise is confirmed.

Health systems warn patients about MyChart-brand phishing emails
health-it1 month ago

Health systems warn patients about MyChart-brand phishing emails

More than a dozen health systems warn patients about phishing emails that impersonate Epic's MyChart portal to steal personal data; the scammers are abusing the MyChart brand rather than indicating a security breach, and Epic urges patients to verify senders, avoid unknown links, and know that MyChart will never ask for account changes or sensitive information via email.

UK PM Burnham contacted by impersonator posing as Trump's aide
world1 month ago

UK PM Burnham contacted by impersonator posing as Trump's aide

Britain’s Prime Minister Andy Burnham exchanged messages with someone who pretended to be Susie Wiles, a close adviser to Donald Trump. Burnham became suspicious and alerted authorities; Politico first reported the incident, and the British embassy in Washington raised it with the White House. Downing Street did not comment on national security. The article notes ongoing phishing attempts linked to Wiles dating back to a 2025 incident.

Azure Credential Breach Leaks Millions of Enterprise Directory Records
security1 month ago

Azure Credential Breach Leaks Millions of Enterprise Directory Records

A threat actor named TheHatman is selling massive Azure/Entra tenant dumps containing employee records from multiple major companies, including McDonald’s (~1.7M) and Vodafone (~425k), exfiltrated via compromised credentials. The data fields cover names, corporate emails, phone numbers, addresses, job titles, departments, and privileged accounts, enabling targeted BEC and privilege escalation. While the exact intrusion vector isn’t confirmed, researchers link the leaks to Infostealer infections and credential abuse rather than a Azure zero-day. Defenders should monitor for credential exposure, enforce MFA, and review third-party access to Azure directories to mitigate risk.}

Most Android Users Don’t Need Antivirus Apps, Here’s Why
technology1 month ago

Most Android Users Don’t Need Antivirus Apps, Here’s Why

For the vast majority of users, Android’s built‑in protections (Google Play Protect, app sandboxing, regular OS updates, and prudent permission controls) provide solid defense against malware and risky apps, making third‑party antivirus apps largely unnecessary. An antivirus may offer peace of mind for high‑risk users or those who sideload apps, but choose a reputable developer and don’t rely on it alone. Real threats often come from social engineering, fake alerts, insecure public Wi‑Fi, and other attack vectors that antivirus can’t fix; safe habits and, when relevant, a VPN are typically more effective. Older devices without updates may still benefit from additional protection, but updates remain the best defense overall.

DEF CON attendees linked to rogue onboard Wi‑Fi phishing on Delta flight
security1 month ago

DEF CON attendees linked to rogue onboard Wi‑Fi phishing on Delta flight

DEF CON attendees are suspected after Delta Flight 591 (Las Vegas–Atlanta) reportedly encountered a rogue onboard Wi‑Fi network, named “Delta WiFi Fast,” with a phishing landing page designed to harvest credentials. Delta said the unauthorized network was present briefly and that the official onboard Wi‑Fi was offline for about 30 minutes; flight safety was not compromised. The FBI’s Atlanta office is investigating, with no arrests announced at this time.