
HybridPetya Ransomware Bypasses UEFI Secure Boot with CVE-2024-7344 Exploit
TL;DR
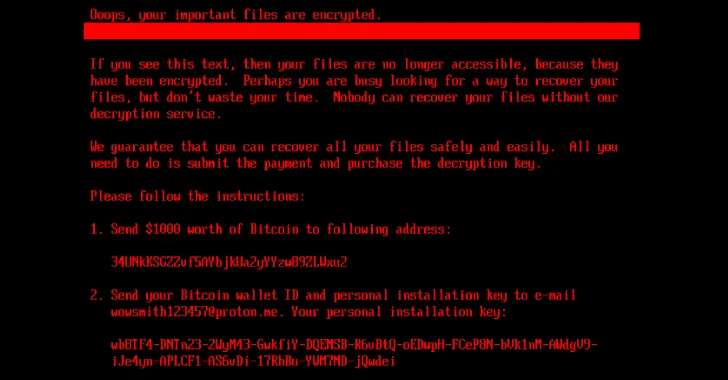
Cybersecurity researchers have discovered HybridPetya, a new ransomware that can bypass UEFI Secure Boot using the patched CVE-2024-7344 vulnerability, by installing malicious EFI applications and encrypting the Master File Table, with capabilities for encryption, ransom demands, and potential decryption, although it has not been observed in active use.
Topics:technologycybersecurity#bootkit#cve-2024-7344#cybersecurity#hybridpetya#ransomware#uefi-secure-boot
- New HybridPetya Ransomware Bypasses UEFI Secure Boot With CVE-2024-7344 Exploit The Hacker News
- Introducing HybridPetya: Petya/NotPetya copycat with UEFI Secure Boot bypass WeLiveSecurity
- ESET Research discovers UEFI-compatible HybridPetya ransomware capable of Secure Boot bypass The Manila Times
- HybridPetya ransomware dodges UEFI Secure Boot theregister.com
- New HybridPetya ransomware can bypass UEFI Secure Boot BleepingComputer
Want the full story? Read the original reporting
Read on The Hacker News