
Malicious npm and Android apps siphon OpenAI Codex tokens in a sophisticated supply-chain attack
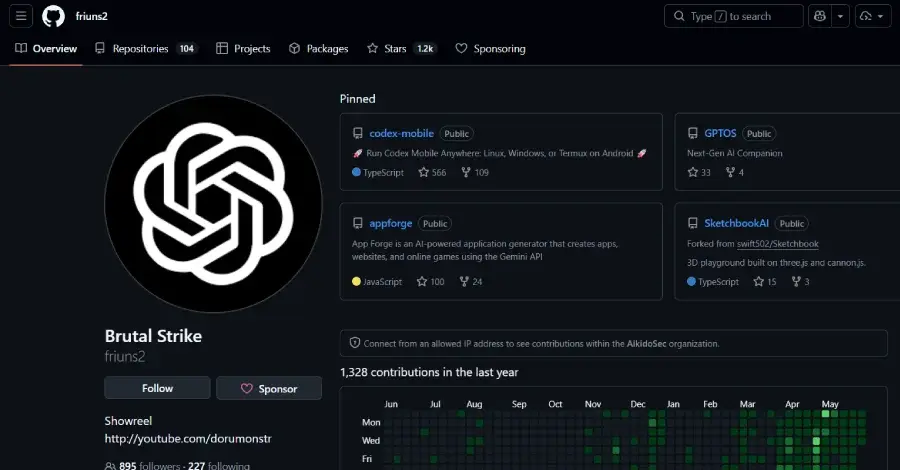
Security researchers uncovered a malicious supply-chain campaign targeting OpenAI Codex via a legitimate-looking npm package (codexui-android) and related Android apps. The npm package, linked to the friuns account (Igor Levochkin), secretly reads Codex credentials from ~/.codex/auth.json and exfiltrates access_token, refresh_token, id_token, and account ID to a server masquerading as Sentry (sentry.anyclaw.store). The refresh_token is long-lasting, enabling persistent access. The same actor also deployed Android apps (OpenClaw Codex Claude AI Agent and Codex) that run the npm package in a PRoot sandbox to harvest credentials. This underscores growing risks to AI developer tooling and software supply chains.
- OpenAI Codex Authentication Tokens Stolen in codexui-android npm Supply Chain Attack The Hacker News
- 27,000-Download Codex UI Tool Secretly Stole OpenAI Refresh Tokens Hackread
- Legitimate-Looking Codex Remote UI Secretly Steals Your AI Tokens Aikido Security
- Legitimate-Looking Codex Remote UI Steals OpenAI Codex Authentication Tokens CyberSecurityNews
- Fake Codex Remote UI Steals OpenAI Auth Tokens gbhackers.com
Want the full story? Read the original reporting
Read on The Hacker News