
Security researchers neutralize dormant Popcorn Time updaters to prevent potential botnet
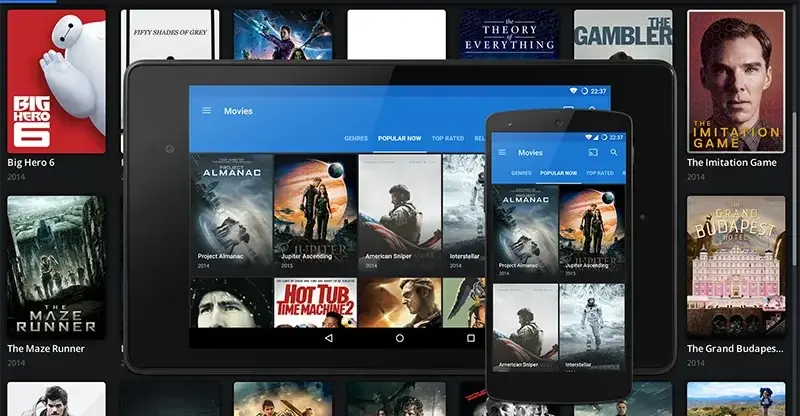
Researchers from Eye Security discovered that abandoned updaters for the defunct piracy app Popcorn Time remained active on millions of devices. These updaters, running on Windows, macOS, and Android, communicated via unencrypted HTTP to abandoned domains, creating a significant risk for botnet recruitment. To mitigate this, the team registered the domains and pushed a self-disabling update, neutralizing the threat without deleting user files. By March, over 2 million update downloads had been distributed before the domains were transferred to the Shadowserver Foundation.
Key points
- Eye Security identified that the updater for the 'Time4Popcorn' fork of Popcorn Time was still active on numerous devices globally.
- The vulnerable software used unencrypted HTTP and outdated Chrome versions, allowing potential attackers to install arbitrary software with full privileges.
- Researchers registered the abandoned domains to push a patch that disabled the updater service on Windows and macOS, though Android devices required manual user interaction.
- The solution faced initial hurdles when security software flagged the fix as malware, but over 2 million updates were successfully distributed by March.
- The domains used for the fix were subsequently transferred to the Shadowserver Foundation to ensure long-term security.
Background
Popcorn Time was a popular torrent streaming application in the 2010s, often described as a 'Netflix for piracy.' Although development ceased years ago, the software remained installed on many devices. This incident highlights the lingering risks of abandoned software, a concern that aligns with broader discussions on digital hygiene and the removal of obsolete applications, similar to recent trends in physical friction devices aimed at reducing digital clutter.
Why it matters
This incident underscores the persistent security risks posed by abandoned software that remains installed on user devices. Even without active development, such applications can serve as vectors for large-scale botnets if their communication channels are compromised. The proactive measure taken by security researchers demonstrates the importance of neutralizing dormant threats before they can be exploited, protecting millions of users from potential surveillance or unauthorized software execution.
What to watch
The domains used to disable the vulnerable updaters have been transferred to the Shadowserver Foundation, ensuring they remain controlled by a security non-profit. Users are advised to uninstall any remaining Popcorn Time or Time4Popcorn software to eliminate residual risks. Security firms may continue to monitor for similar abandoned software vulnerabilities that could be exploited for botnet creation.
Want the full story? Read the original reporting
Read on The Verge