
Atera Windows Installers Vulnerable to Critical Privilege Escalation Attacks
TL;DR
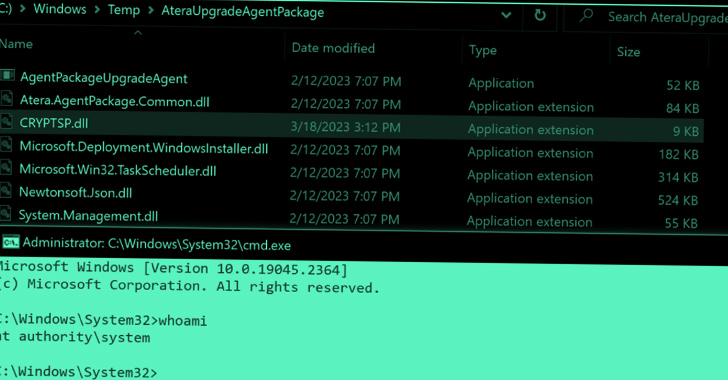
Zero-day vulnerabilities in the Windows Installers for Atera's remote monitoring and management software have been discovered, posing a risk of privilege escalation attacks. The flaws, assigned CVE-2023-26077 and CVE-2023-26078, have been patched in Atera versions 1.8.3.7 and 1.8.4.9. The vulnerabilities allow for the execution of arbitrary code with elevated privileges and involve misconfigured Custom Actions running as NT AUTHORITY\SYSTEM. Exploitation of these weaknesses could lead to local privilege escalation attacks.
Topics:technologywindows-security#atera#privilege-escalation#vulnerabilities#windows-installers#windows-security#zero-day
Want the full story? Read the original reporting
Read on The Hacker News