
Simultaneous Cyberattacks on Russian and Ukrainian Emergency Apps Spark False Nuclear Alerts
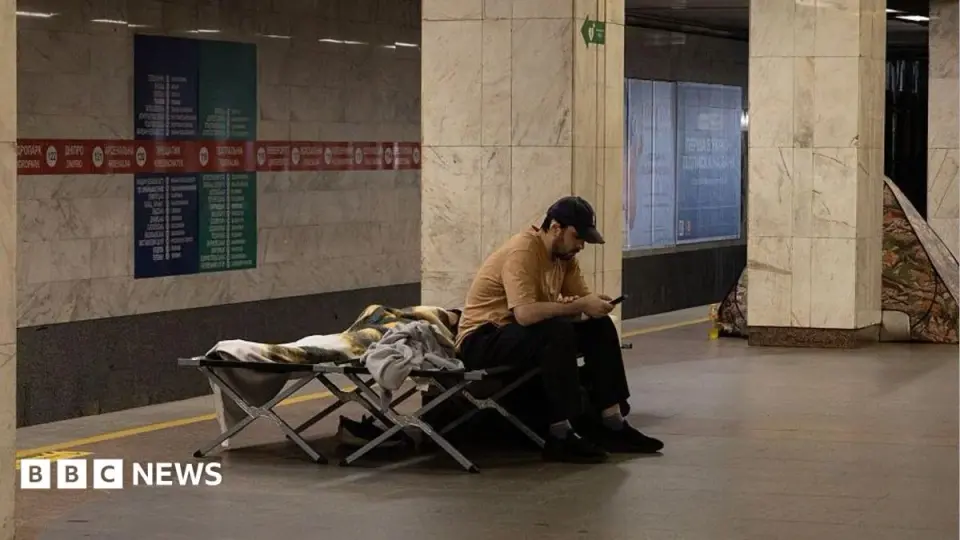
Emergency alert applications in both Russia and Ukraine were compromised by apparent cyberattacks on November 1, 2026. The breaches resulted in the distribution of false warnings regarding nuclear strikes, chemical hazards, and radiation threats. Ukrainian authorities blamed Moscow for the intrusion, while Russian officials confirmed a 'massive cyberattack' but did not immediately identify the perpetrator. The incidents occurred shortly after the conclusion of a six-day humanitarian ceasefire in the occupied city of Oleshky.
Key points
- Ukraine's air raid alert app displayed fake messages warning of radiation and chemical attacks in Kyiv, as well as the deployment of the Russian Oreshnik hypersonic missile.
- Russia's emergency ministry reported that its mobile application was hacked, allowing attackers to send false information to the public, including warnings about nuclear warheads.
- Ukraine's Center for Strategic Communications attributed the hack to Russia, urging citizens to disregard 'strange messages' and rely on official channels.
- Russian officials stated that while the app was compromised, the broader public alert system, which includes sirens and broadcasts, remained operational.
- The cyber incidents followed the end of a six-day ceasefire in Oleshky, a Russian-occupied city, which had facilitated the evacuation of hundreds of civilians.
Background
These digital attacks occur amidst escalating tensions in the Russia-Ukraine conflict. Recent weeks have seen significant strikes on energy infrastructure, including Russian drone attacks that left hundreds of thousands of Ukrainians without power on November 1. Additionally, the cyber incidents follow a rare six-day humanitarian ceasefire in Oleshky, brokered with the assistance of US First Lady Melania Trump and Pope Leo XIV, which was the longest truce since the start of the full-scale invasion.
How outlets are covering it
Ukrainian officials, including the Center for Strategic Communications and the Air Force, explicitly blamed Russia for the cyberattack, describing it as 'hostile interference' and 'enemy influence.' In contrast, Russian authorities acknowledged a 'massive cyberattack' on their emergency app but did not publicly attribute the incident to a specific actor. Fox News highlighted the use of hybrid tactics, noting that such cyber operations may be part of a broader strategy to destabilize civilian infrastructure. Al Jazeera emphasized the timing of the attacks, linking them to the immediate aftermath of the Oleshky ceasefire, suggesting the digital strikes may have been intended to disrupt the humanitarian mission or sow panic as fighting resumed.
Why it matters
The compromise of emergency alert systems undermines public trust in critical safety infrastructure during an active conflict. False warnings of nuclear and chemical threats can cause widespread panic and hinder emergency response efforts. Furthermore, the simultaneous targeting of both nations' digital alert systems highlights the increasing role of cyber warfare in hybrid conflicts, where digital intrusions are used to complement kinetic military operations and psychological warfare.
What to watch
Authorities in both countries are working to restore the functionality of their respective emergency apps. Ukraine has urged citizens to monitor official channels for accurate information, while Russia is restoring its mobile application. The resumption of fighting in Oleshky is expected to continue, with both sides accusing each other of using the ceasefire period to strengthen frontline forces. Future cyber incidents may target other critical infrastructure as the conflict evolves into a more complex hybrid war.
- Russia says emergency alert app under cyber-attack after apparent hack on Ukraine's warning system BBC
- Ukraine says air alert system hacked after false radiation warning in Kyiv Fox News
- Ukraine blames Russia after air alert app sends out false warnings Al Jazeera
- Russian emergencies ministry's mobile app hit by cyberattack, TASS says Reuters
- Ukraine, Russia report hacking attacks on emergency alert apps after Oleshky truce ends DW.com
Want the full story? Read the original reporting
Read on BBC