Tag

Zero Click

All articles tagged with #zero click

AI-crafted WeChat worm hijacks accounts via ringless calls
technology29 days ago

AI-crafted WeChat worm hijacks accounts via ringless calls

Researchers at Calif say they used AI to develop WeWorm, a zero-click worm that hijacks a WeChat account during an incoming call by exploiting a memory-bug in WeChat’s calling stack, then automatically calls the victim’s contacts to spread. The attacker must be on the victim’s friend list, and once in, can read and send messages and perform actions as the owner. Tencent says the flaw was fixed and that no users were reported affected; no CVE or public advisory has been released. The team built the exploit in roughly two weeks after bug discovery, with a demo in August, and plans a full analysis for a conference. The case underscores AI-enabled attack risks and comes as EU cyber-resilience rules push for disclosure requirements.
Zero-Click WeChat Worm Hijacks Accounts Through Incoming Calls
technology1 month ago

Zero-Click WeChat Worm Hijacks Accounts Through Incoming Calls

Researchers from Calif demonstrated a zero-click worm that hijacks a WeChat account via an incoming call from a trusted contact, without the user answering. Once the exploit runs, the attacker can read and send messages, make calls, and act as the account owner, though only the account and not the device is compromised. Tencent patched the bug with Android/iOS updates and blocked the exploit on its servers; no real-world attacks have been reported. The attack relies on the caller being in the contact list, and full technical details will be released later.

Microsoft Addresses Multiple Zero-Day Vulnerabilities in May 2023 Patch Tuesday
cybersecurity3 years ago

Microsoft Addresses Multiple Zero-Day Vulnerabilities in May 2023 Patch Tuesday

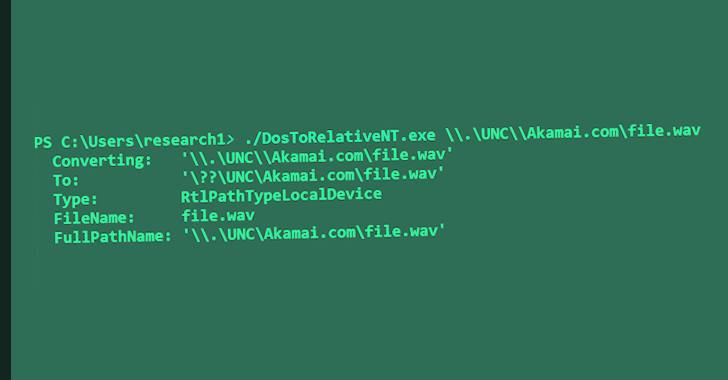
Cybersecurity researchers have disclosed a zero-click vulnerability in Windows MSHTML platform that could be exploited to bypass integrity protections on targeted machines and steal NTLM credentials. The vulnerability, tracked as CVE-2023-29324, affects all Windows versions and is a bypass for a fix Microsoft put in place in March 2023 to resolve CVE-2023-23397. Microsoft has addressed the vulnerability as part of its Patch Tuesday updates for May 2023 and is recommending users to install Internet Explorer Cumulative updates to address vulnerabilities in the MSHTML platform and scripting engine.