
OpenSSH 10.6p2 Patches Critical 'SSHole' Flaw Allowing Login Bypass on Alpine Linux
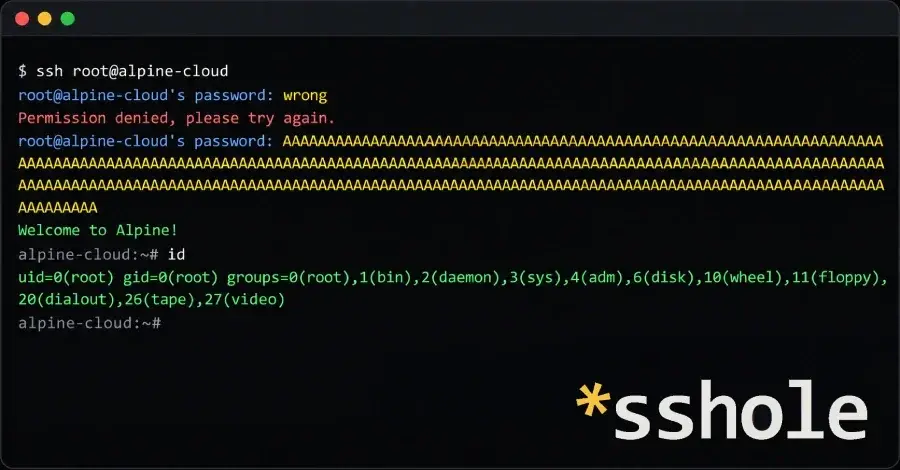
OpenSSH released version 10.6p2 to fix a critical flaw allowing attackers to bypass authentication on Alpine Linux servers. The vulnerability, dubbed 'SSHole,' affects systems using the musl C library without PAM, where long passwords trigger a false positive in password verification. No active exploitation has been reported, but immediate patching is advised.
Key points
- OpenSSH released version 10.6p2 to address a critical authentication bypass flaw.
- The vulnerability affects Alpine Linux and other musl-based systems not using PAM.
- Attackers can log in by submitting a password between 257 and 1,024 bytes long.
- The flaw exploits a mismatch between musl's crypt() error handling and OpenSSH's salt borrowing.
- No CVE identifier has been assigned, and no active exploitation has been reported.
- Alpine Linux has published fixed packages for all releases back to version 3.16.
Background
This incident follows a series of critical security patches in late 2026, including fixes for .NET Brotli decoder flaws and Tailscale SSH forwarding issues. It also follows Alpine Linux's recent rebuild of its GitLab server after a failed attack on a regex engine vulnerability. The current issue highlights ongoing challenges in authentication mechanisms for lightweight Linux distributions.
How outlets are covering it
The Hacker News and CyberSecurityNews emphasize the technical specifics of the musl and OpenSSH interaction, noting the flaw has existed since 2016. BleepingComputer highlights the discovery by researcher Ozgun Kultekin using AI agents. Tom's Hardware focuses on the broad impact across distributions like OpenWrt and Yocto, noting that OpenWrt is less affected due to its default use of Dropbear. All sources agree on the need for immediate patching or disabling password authentication.
Why it matters
The vulnerability affects a wide range of systems, including containers and cloud instances, potentially exposing millions of devices. The ease of exploitation, requiring only a long password and a known account name, makes it a significant risk for any unpatched Alpine Linux server. The flaw's presence in default configurations of cloud images increases the urgency for remediation.
What to watch
Administrators should update OpenSSH to version 10.6p2 or later, or disable password authentication immediately. They should also review logs for unauthorized password logins and check for compromised accounts. OpenSSH and Alpine Linux continue to monitor for any signs of exploitation.
- OpenSSH Issues Emergency Fix for Flaw Letting Long Passwords Bypass SSH Auth on Alpine Linux The Hacker News
- OpenSSH flaw lets attackers log into password-disabled Linux accounts BleepingComputer
- Combined flaws let anyone into Alpine Linux and other distros by typing anything over 256 characters as a password — emergency fixes for OpenSSH and musl-libc issued for millions of systems, patch immediately Tom's Hardware
- OpenSSH Flaw Could Let Attackers Bypass Password Authentication on Alpine Linux Servers CyberSecurityNews
- OpenSSH and Alpine Linux warn of severe but niche bug heise online
Want the full story? Read the original reporting
Read on The Hacker News