Tag

Artex

All articles tagged with #artex

FBI Warns ARTEX AI Framework Enables Machine-Speed Intrusions Across Global Sectors
cybersecurity7 hours ago

FBI Warns ARTEX AI Framework Enables Machine-Speed Intrusions Across Global Sectors

The FBI issued a flash advisory warning that the open-source AI tool ARTEX is being weaponized to automate cyberattacks. Since August 2026, attackers have used the framework to breach organizations in finance, energy, and government sectors, achieving privileged access in under three hours. Notable incidents include a South Korean financial breach exposing data for 67,000 people and a supply-chain attack affecting over 2,250 ConnectWise Cloud Backup tenants. Although the creator removed the code in October, forks remain available, prompting the FBI to urge organizations to reduce internet-facing attack surfaces and monitor for unusual activity.
FBI Warns Open-Source AI Tool ARTEX Enables Machine-Speed Cyber Intrusions
technology8 hours ago

FBI Warns Open-Source AI Tool ARTEX Enables Machine-Speed Cyber Intrusions

The FBI issued a flash advisory warning that the open-source AI framework ARTEX is being weaponized to automate cyber intrusions at machine speed. Since August 2026, threat actors have used the tool to target sectors including finance, government, and healthcare, with some attacks achieving privileged access in under three hours. Although the creator removed the code in October, forks remain available, and campaigns have already compromised South Korean banks and supply chain vendors.

FBI and vendors detail ARTEX AI framework enabling machine-speed intrusions across global sectors
cybersecurity10 hours ago

FBI and vendors detail ARTEX AI framework enabling machine-speed intrusions across global sectors

The FBI issued a FLASH advisory warning that the open-source ARTEX framework is being weaponized to automate complex cyber intrusions at machine speed. Originally released in July 2026, the tool uses large language models to execute reconnaissance, exploitation, and data exfiltration with minimal human input. Despite the developer removing the repository in October, community forks and commercial versions remain widely available. Recent incidents include a supply chain compromise affecting ConnectWise Cloud Backup, which impacted over 2,250 downstream tenants, and attacks on South Korean financial institutions that exposed data for approximately 67,000 individuals. The framework lowers the barrier for sophisticated attacks, enabling small threat groups to conduct large-scale operations against energy, manufacturing, and telecom sectors.

FBI Warns AI Hacking Tool ARTEX Is Automating Global Intrusions at Machine Speed
cybersecurity1 day ago

FBI Warns AI Hacking Tool ARTEX Is Automating Global Intrusions at Machine Speed

The FBI issued a flash advisory warning that the open-source AI framework ARTEX is being weaponized by threat actors to automate complex cyberattacks across multiple sectors. Originally released in July 2026, the tool allows users to integrate various large language models to perform reconnaissance, exploitation, and data theft with minimal human intervention. Although the creator removed the repository in October 2026, community forks and commercial versions continue to proliferate. The FBI notes that ARTEX enables attackers to achieve privileged access in under three hours, targeting overlooked systems like partner portals and legacy services. Recent incidents include a supply-chain breach affecting Microsoft 365 customers and attacks on South Korean financial institutions.

Amazon Threat Intelligence Exposes AI Agent Campaigns Harvesting API Keys via ARTEX
cybersecurity1 day ago

Amazon Threat Intelligence Exposes AI Agent Campaigns Harvesting API Keys via ARTEX

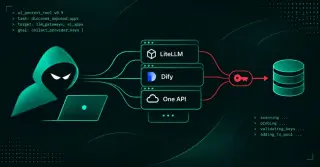
Amazon’s threat intelligence team identified coordinated campaigns using AI agents to steal API keys from internet-exposed applications like LiteLLM and Dify. The attacks, likely linked to China-based groups, exploit default credentials and unpatched vulnerabilities. Cloudflare and the FBI have also reported increased activity involving the ARTEX framework, highlighting a shift toward automated, persistent cyber intrusions.

Storm-0940 Leverages AI Agents for Rapid Supply Chain Breach of ConnectWise
cybersecurity27 days ago

Storm-0940 Leverages AI Agents for Rapid Supply Chain Breach of ConnectWise

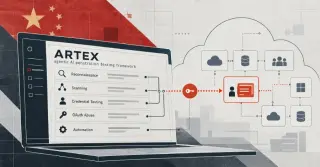
Microsoft identified the China-linked threat actor Storm-0940 as the perpetrator behind a supply chain compromise of ConnectWise Cloud Backup. The group utilized ARTEX, an agentic AI penetration testing framework, to automate reconnaissance and credential abuse at machine speed. This allowed attackers to bypass interactive sign-ins and gain privileged access to hundreds of global organizations across various sectors. The campaign, active since September 2026, involved massive password-spraying attempts against Microsoft 365 tenants, with some breaches achieving privileged access in under three hours. ConnectWise has suspended services to mitigate the threat, while Microsoft warns that AI-driven attacks significantly reduce the time between initial targeting and successful compromise.