Tag

Exploit Kit

All articles tagged with #exploit kit

BlueMoon Exploit Kit Triggers Espionage Wave Across Four Groups
security1 month ago

BlueMoon Exploit Kit Triggers Espionage Wave Across Four Groups

Proofpoint links a new Chrome/Windows exploit kit, BlueMoon, to a wave of espionage campaigns by four groups—primarily China-aligned—using two Chrome V8 flaws (CVE-2026-85046 and CVE-2026-85880) and a Windows ALPC privilege escalation to run payloads after a phishing lure; multiple variants target NGOs, aerospace, Vietnamese manufacturing, and government/financial sectors, with DLL sideloading, Cloudflare infrastructure, and in-memory payloads observed. CISA added the Chrome flaw to Known Exploited Vulnerabilities; patching browsers may not remove implants. Indicators include process chains (chrome.exe → cmd.exe → curl.exe → msgbox.exe), ChromeUpdate.exe/msgbox.exe in %TEMP%, specific scheduled tasks (EdgeCore_AutoUpdate, MicrosoftEdgeUpdatesTaskMachine, Avpcheckup, GeForceService), a registry key, and related DLL artifacts; detection rules 2071919–2071924 published.
BlueMoon Exploit Kit Exploits Patch Gap Across Four Groups
technology1 month ago

BlueMoon Exploit Kit Exploits Patch Gap Across Four Groups

Proofpoint researchers identify BlueMoon, a near-identical exploit kit chaining two Chromium V8 flaws and a Windows kernel vulnerability to drop malware, used by at least four groups (TA412 and three other China-aligned actors) against NGOs, mining firms, traders, and aerospace targets. The campaign leveraged a Chromium patch gap and AI-assisted vulnerability discovery, exploiting CVE-2026-85046 and CVE-2026-85880 with patches issued within 24 hours, and may continue to spread as Chromium-based browsers are updated.

Leaked DarkSword Kit Powers a Global iOS GHOSTBLADE Campaign
technology2 months ago

Leaked DarkSword Kit Powers a Global iOS GHOSTBLADE Campaign

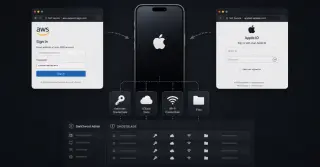
An unknown Chinese-speaking threat actor is using a publicly leaked DarkSword exploit kit to deploy GHOSTBLADE on iOS devices (versions 18.4–18.7) via watering-hole sites and fake sign-in portals. The attack chain loads JavaScript through malicious iframes to execute the kit, exfiltrating keychain, iCloud, and Wi‑Fi credentials to attacker-controlled endpoints. Multiple DarkSword admin panels are hosted across Hong Kong, Singapore, and other regions, with ties to other tools and groups, signaling expanded use of the kit since the leak (including indicators linked to UNC6353). The operation also references additional tooling and decoy pages, highlighting a broader, evolving threat landscape against iOS targets.

DarkSword: High-End iOS Exploit Kit Uses Zero-Days for Rapid Device Takeover
security6 months ago

DarkSword: High-End iOS Exploit Kit Uses Zero-Days for Rapid Device Takeover

DarkSword is a JavaScript-based iOS exploit kit targeting iPhones on iOS 18.4–18.7 via watering-hole campaigns, chaining six vulnerabilities to achieve remote code execution, escaping the WebContent sandbox through the GPU into mediaplaybackd, escalating to kernel privileges, and then loading a data-collection module to exfiltrate a wide range of information (including emails, iCloud data, messages, wallet data, photos, contacts, and more) before cleaning up. Used by UNC6353 and linked groups such as UNC6748 and PARS Defense, the kit underscores a growing market for high-end iOS exploits and rapid, non-persistent data theft.