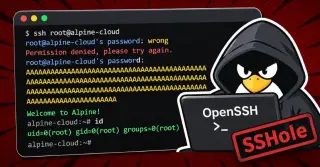
Active Exploitation of 'SSHole' Flaw Compromises Alpine Linux Servers
A critical vulnerability known as 'SSHole' is under active exploitation, allowing attackers to bypass authentication on Linux systems using the musl C library. The flaw, tracked as CVE-2026-123158, affects OpenSSH when configured without Pluggable Authentication Modules (PAM). Attackers can gain root access by submitting oversized passwords to accounts with no password set. OpenSSH and Alpine Linux have released emergency patches, urging immediate updates to prevent compromise.