
AI-Generated PowerShell Tool Maps Active Directory in Rapid Breach
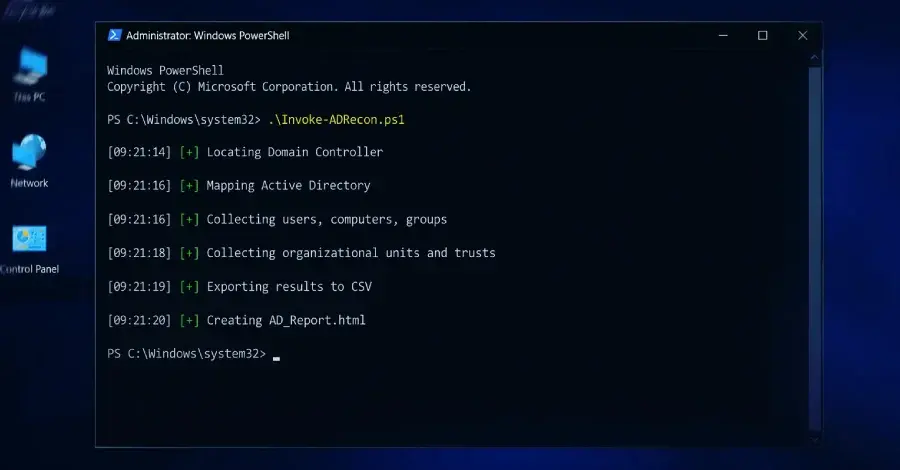
Cybersecurity researchers flag a June 2026 intrusion where attackers used an AI-generated, vibe-coded PowerShell script to enumerate a Windows Active Directory after gaining RDP access to a domain-joined server. The tool locates the Domain Controller, maps AD users, computers, groups, OUs, and trusts, creates a staging area, and exports results (including AD_Report.html). Attackers then deployed s5cmd and SharpShares to locate data repositories, exported data to CSV, archived it, and exfiltrated it to a remote server. The incident highlights how AI-assisted tooling lowers entry barriers and accelerates reconnaissance, aligning with established smash-and-grab playbooks, while a related Sygnia report notes AI-enabled cloud intrusions can scale quickly using credentials and cloud weaknesses rather than new malware.
- Attacker Uses Suspected AI-Generated PowerShell Script to Map Active Directory The Hacker News
- Experts warn hackers are using AI chatbots to write malware using natural language TechRadar
- Hackers Using Vibe-Coded Generated PowerShell Script to Enumerate Active Directory Accounts CyberSecurityNews
- Threat actor uses AI-generated malware in network intrusion SC Media
- Hackers Are Using AI Vibe Coding To Build Custom Malware TechRound
Want the full story? Read the original reporting
Read on The Hacker News