Tag

Bug Bounty

All articles tagged with #bug bounty

Hackers Exploit Claude to Breach OpenAI in Under 72 Hours
security21 days ago

Hackers Exploit Claude to Breach OpenAI in Under 72 Hours

A trio of independent researchers named Hacktron used Anthropic’s Claude AI (Opus 4.8 and then Opus 5) to break into OpenAI systems by exploiting a Discourse image-upload bug and an OpenAI SSO flaw. They accessed an internal OpenAI discussion forum containing employee authentication tokens, potentially enabling further access to ChatGPT, Codex, Outlook, Slack, GitHub, and more. They proved their presence with a pull request to OpenAI’s internal codebase. The operation took place within 72 hours of discovery, and the researchers were paid $6,500 through OpenAI’s bug bounty program, highlighting how even AI builders can be vulnerable to sophisticated, human-guided exploits.
Claude-powered ethical hack reveals OpenAI security gaps
technology22 days ago

Claude-powered ethical hack reveals OpenAI security gaps

Hackers from Hacktron AI used Anthropic’s Claude and OpenAI’s GPT-5.6 Sol to ethically breach a subset of OpenAI staff ChatGPT accounts, enabling access to a software cache via an internal staff forum and a harmless GitHub pull request; OpenAI patched the vulnerabilities after the disclosure and paid a $6,500 bug bounty, illustrating how AI tools can speed up complex cyberattacks and fueling ongoing safety debates in the industry.

Security researchers breach OpenAI using rival tooling, spotlighting AI security gaps
technology22 days ago

Security researchers breach OpenAI using rival tooling, spotlighting AI security gaps

Cybersecurity researchers from Hacktron AI exploited a flaw in OpenAI’s community forum to access an OpenAI employee’s ChatGPT account and read internal code, using Anthropic’s security tool as part of their assessment. OpenAI fixed the issues and paid the researchers $6,500 under a bug-bounty program, highlighting persistent security vulnerabilities as AI labs scale their tools and regulators scrutinize model safety.

Apple Tightens Bug-Bounty Submissions After AI-Generated Flood
technology2 months ago

Apple Tightens Bug-Bounty Submissions After AI-Generated Flood

Apple has limited the number of open bug-bounty submissions after a surge of AI-generated, low-quality reports clogs its review system. A security firm using ChatGPT surfaced dozens of macOS bugs but was limited by Apple’s caps, though researchers can request higher limits for critical issues. While AI helps parse submissions, Apple maintains large rewards for real exploits, with prizes up to $2 million and potential bonuses over $5 million; the company notes AI has both aided discovery and auditing of reports.

Apple tightens bug-report flood as AI-generated findings surge
technology2 months ago

Apple tightens bug-report flood as AI-generated findings surge

Apple has capped the number of open vulnerability reports through its internal security portal and instituted a 30‑day cooldown to curb a surge of AI-generated submissions, part of a broader move to accelerate security updates. Researchers can request higher quotas for critical reports; the policy follows industry trends and high‑profile AI-assisted findings, including Calif.io’s macOS kernel exploit work, with Apple engaging affected researchers like Bynario and noting ongoing bug-bounty adjustments across the sector.

Six-figure bounty awarded for Linux KVM guest-to-host escape flaws
security3 months ago

Six-figure bounty awarded for Linux KVM guest-to-host escape flaws

Google paid $250,000 for Januscape (CVE-2026-53359), a use-after-free flaw in Linux KVM's shadow MMU that can let a malicious guest VM break out and gain root on the host; a separate flaw, GhostLock (CVE-2026-43499), lets limited users escalate to root via futex priority-inheritance. Patches are in the Linux kernel, and users should update to mitigate the risk.

AMD's bounty controversy: researcher denied reward as updater flaw patched after 124 days
technology4 months ago

AMD's bounty controversy: researcher denied reward as updater flaw patched after 124 days

Security researcher MrBruh disclosed a remote-code-execution flaw in AMD's auto-updater; AMD initially dismissed it as out of scope, delayed a bounty for 124 days, and then changed rules about disclosure. The vulnerability could enable MITM via plain HTTP links; AMD patched Ryzen Master, µProf, and Management Console (CVE-2026-40677). AMD now says updates use HTTPS and have signature verification, but the researcher notes the check is weak (CRC32) and a redirection bug could affect self-updating; users should manually install the latest versions from AMD’s site.

AI-Fueled Bug Hunt Redraws the Security Patch Landscape
security4 months ago

AI-Fueled Bug Hunt Redraws the Security Patch Landscape

AI agents are increasingly autonomously finding software flaws and crafting exploits, upending bug-bounty economics as researchers log far more discoveries and attackers speed up development. Major programs are trimming or shifting payouts (Curl’s bounty ended; Google adjusted Chrome/Android rewards) and experts warn that faster zero-days and compressed disclosure windows could pressure quicker patches. The trend, including industry calls for structural defenses and architecture changes, suggests a future where human-led bug hunting remains essential but must be complemented by better-infrastructure that makes many bugs irrelevant.

Google boosts Android/Chrome bug-bounty rewards to as high as $1.5M
technology5 months ago

Google boosts Android/Chrome bug-bounty rewards to as high as $1.5M

Google overhauls its Android and Chrome vulnerability rewards programs, elevating top Android payouts to $1.5 million for zero-click full-chain exploits on the Pixel Titan M2 (with up to $750,000 for non-persistent variants) and offering up to $250,000 for Chrome full-chain exploits plus a $250,128 bonus for MiraclePtr-protected memory allocations; the changes push for concise bug proofs instead of lengthy analyses and narrow Android focus to Linux kernel vulnerabilities in Google components unless researchers demonstrate device exploitability. The revamp follows a record 2025 with $17.1 million paid to 747 researchers, bringing total payouts since 2010 over $81.6 million, and 2026 totals are expected to rise despite some reductions.

GitHub patches critical AI-discovered RCE in under six hours
technology5 months ago

GitHub patches critical AI-discovered RCE in under six hours

Wiz Research used AI to uncover a critical remote-code-execution vulnerability in GitHub’s internal git infrastructure. GitHub’s security team reproduced the issue within 40 minutes, developed a fix, and deployed it to github.com and GitHub Enterprise Server within about six hours total. No exploitation was found. The flaw was described as remarkably easy to exploit, highlighting the importance of rapid response, and it follows recent outages and reliability concerns at GitHub.

DJI Shells Out $30K for Romo Hack Discovery, Promises Faster Security Upgrades
technology7 months ago

DJI Shells Out $30K for Romo Hack Discovery, Promises Faster Security Upgrades

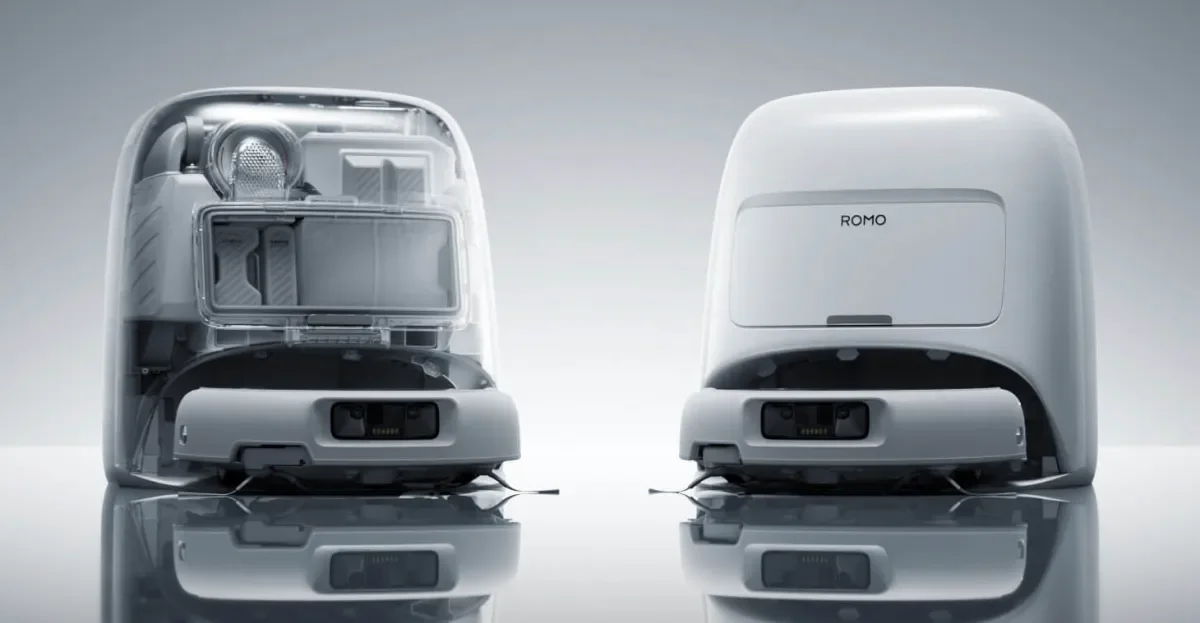
DJI will pay security researcher Sammy Azdoufal $30,000 for a discovery related to vulnerabilities in the Romo robot vacuum network, including a fix for a PIN-free video viewing issue. The company says it has already addressed the vulnerability and will roll out further upgrades within a month, while continuing security testing, third‑party audits, and new ways for researchers to collaborate.

AI Slop Sinks cURL Bug Bounties, Stenberg Says
technology8 months ago

AI Slop Sinks cURL Bug Bounties, Stenberg Says

Daniel Stenberg, lead developer of cURL, is ending the project's bug bounty program at the end of January due to a flood of low-quality AI-assisted submissions he dubs "AI slop." While AI can aid bug discovery, the volume and quality of reports have overwhelmed maintainers, prompting the move even as genuine issues are still welcome under strict AI usage rules.